Field notes / MadHacks 2026 / Madison, WI

Owl

Finds what's wrong with your internet, and catches a network that lies.

Owl is an Android app. It digs down through your Wi-Fi, your router, DNS and the internet, and tells you in plain words whether the trouble is your Wi-Fi, your router or your provider. When the network lied to you, it shows the proof. No report leaves your phone unless you send it.

Get the app Who it's for How it proves a lie

A block of ground cut open under a house. Four layers from top to bottom: Wi-Fi, Router, DNS and Internet. A drill runs down from the house through Wi-Fi and Router and stops in the DNS layer, which is cracked and glowing orange.the drill stops hereLAYER 1Wi-FicleanLAYER 2RoutercleanLAYER 3DNSfake answersLAYER 4Internetnot reached
Fig. 1. A home connection, cut top to bottom. This one has a router that hands out fake answers.

Sample 01 / The problem / April 7, 2026

In April, the FBI had to reset hijacked routers in the US.

On April 7, 2026, the Justice Department and the FBI ran a court-authorized operation. It sent hijacked TP-Link routers in the US commands that, in the department's words, force routers to obtain legitimate DNS resolvers from their Internet Service Providers (ISP).1

The Justice Department says Russian military intelligence, GRU Unit 26165, had been stealing the logins for thousands of TP-Link routers worldwide since at least 2024.1 The head of the FBI's Boston office said the GRU weaponized routers in more than 23 states.1

DNS is the phone book of the internet. Your phone asks it where a website lives. A hijacked router points every device in the house at a phone book the attacker wrote. The UK's National Cyber Security Centre says the changed settings were subsequently inherited by downstream devices, for example laptops and phones.3

Microsoft counted over 200 organizations and 5,000 consumer devices hit by the attackers' DNS servers. In the targeted cases, it says, the attackers' server would then present an invalid TLS certificate.2 That bad certificate is the signal Owl looks for.

None of this is new. In 2011 the DNSChanger malware re-routed more than four million computers.5 And it will keep happening. In March 2026 the FCC put new foreign-made consumer router models on its Covered List, but the action does not impact a consumer's continued use of routers they previously acquired.6 The old router in the closet stays in the closet.

The FBI said it was working with ISPs to provide notice to router owners.1 So the internet provider is part of the fix. Owl is built for both ends of that phone call.

thousands
of TP-Link routers worldwide with stolen logins, says the Justice Department. It gives no exact count.1
more than 23
states where the GRU weaponized routers, says the FBI's Boston office.1
5,000
consumer devices, and over 200 organizations, hit by the attackers' DNS servers. Microsoft's count.2
18,000
IP addresses, in at least 120 countries, seen talking to the attackers' infrastructure at the December 2025 peak. Lumen counted addresses, not routers.4

Sample 02 / The method / Layer 3, DNS

How Owl proves a lie

A different address proves nothing. Big sites hand out different addresses all day. So Owl makes the address prove who it is.

  1. Step 1 / Ask twice

    Ask the network, then ask around it

    Owl asks the network's DNS where a site lives. Then it asks Cloudflare and Google, plus Quad9 on Android 14 and up, the same thing over encrypted DNS. It reaches them by IP address and checks their certificates, so the router has no say in it. An address is trusted if any of them returned it. Anything else has to prove itself with a certificate.

    The network said
    tdstelecom.com
    is at 10.42.0.1
    Encrypted DNS said
    tdstelecom.com
    is at 203.0.113.20

    Different. That is a question, not proof.

  2. Step 2 / The certificate check

    Make the address prove who it is

    Owl connects to the address the network gave and asks for the site's certificate. It checks that certificate against the phone's own list of trusted signers, and nothing else. A real server passes. A fake one does not.

    Asked 10.42.0.1 to prove it is tdstelecom.com
    shown as CN=dig-demo
    signed by CN=dig-demo
    not signed by anyone the phone trusts

    Fake, with proof

    Owl calls an address fake when it fails the certificate check for the name, or when it refuses the connection outright while the real address proves itself. If the real one shows the same certificate or a bad one of its own, a bad certificate proves nothing. An address that only times out gets a warning, because a slow network looks the same.

  3. Step 3 / The control

    Check that the check is fair

    On the same network, google.com came back with a different address too. That is normal. Owl put that address through the same test, and it proved it is google.com. tdstelecom.com couldn't.

    The network said
    google.com
    is at an address encrypted DNS did not give
    Asked that address to prove it is google.com
    valid certificate for google.com

    Different, and real

    A mismatch alone is never called bad. Anything Owl can't settle is a warning or unknown.

Fig. 2. Demo data: one dig on the demo router, top to bottom. 203.0.113.20 is a made-up example address, not the real one for tdstelecom.com. The addresses come from the demo kit, which lies about tdstelecom.com and owl.munzzyy.dev on its own hotspot and nowhere else.

The idea is not mine alone. Comparing a network's answer with a trusted one, and settling it with a TLS handshake, is what OONI Probe does to measure censorship, and I learned it from their spec.9 Owl's part is running it on the phone, treating the failed certificate as the proof, and then doing something about it.

Sample 03 / The fix / Phone, router and provider

What it does about it

A / On the phone

Shield

Shield is a local VPN that carries only DNS. It sends the phone's lookups over HTTPS to an encrypted DNS provider, so the router can't change the answers. Then Owl digs again on its own, and you watch the DNS layer heal. The router layer stays amber until the router itself is fixed.

One option, off by default, has Shield ask only Quad9 and Cloudflare's security service, which refuse names on their own threat lists. Owl keeps no list of its own, and theirs can miss new sites.

Why a VPN? A normal Android app is not allowed to change the phone's Private DNS setting.7 Android also runs one VPN at a time, so Shield can't sit next to another one.8

Two small cross-sections. Before Shield, the DNS layer is cracked and orange. With Shield on, the DNS layer is solid and marked with a green check.beforewith Shield onDNS LAYER, CRACKEDDNS LAYER, HEALED

B / For the support call

The support ticket

One page a support agent can read in 20 seconds: what is wrong, when it was found, the proof, and whether Shield is on. The full raw data rides along as owl-report.json.

You send it yourself, one ticket at a time. It leaves the phone only when you send it.

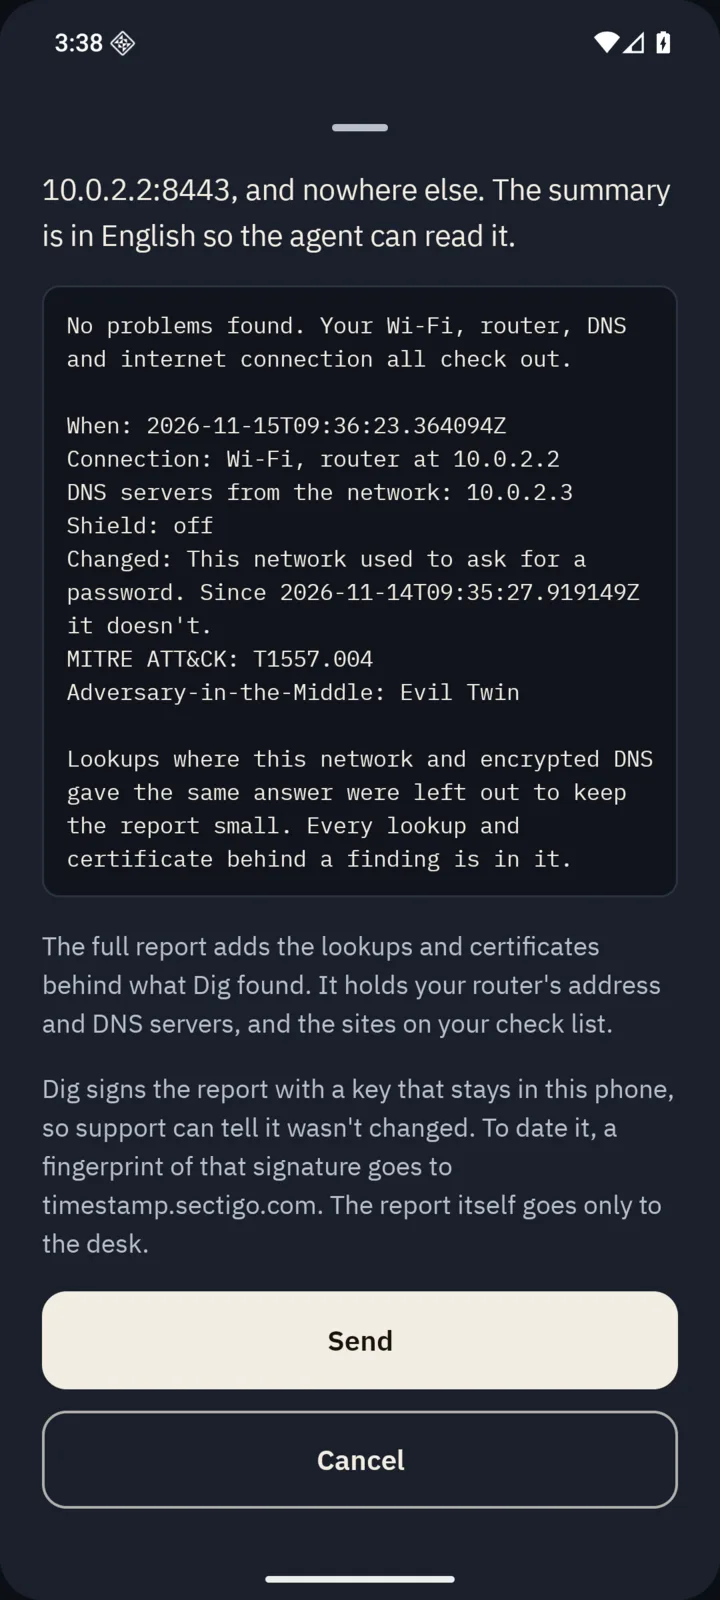
A ticket to a desk is sealed. The phone signs the report with a key kept in the Android Keystore and has the signature time-stamped by a public service. The desk checks both and shows Sealed or Seal broken. The seal says the report wasn't changed and when it existed. The proof inside is what shows the lie.

Ticket T-0003 / Hijack / Demo data

Your router is sending you to fake websites.

tdstelecom.com and owl.munzzyy.dev went to 10.42.0.1, which could not prove it is either site.

Found at 1:12 PM on Wi-Fi. Shield was off.

attached: owl-report.json

C / For the internet provider

The campaign spotter

The support desk groups tickets that name the same rogue DNS server. One ticket looks like one customer's router problem. Two homes pointing at the same server look like a campaign, and the desk says so. That means most when the server is a public address, since every home has its own 192.168.x.x.

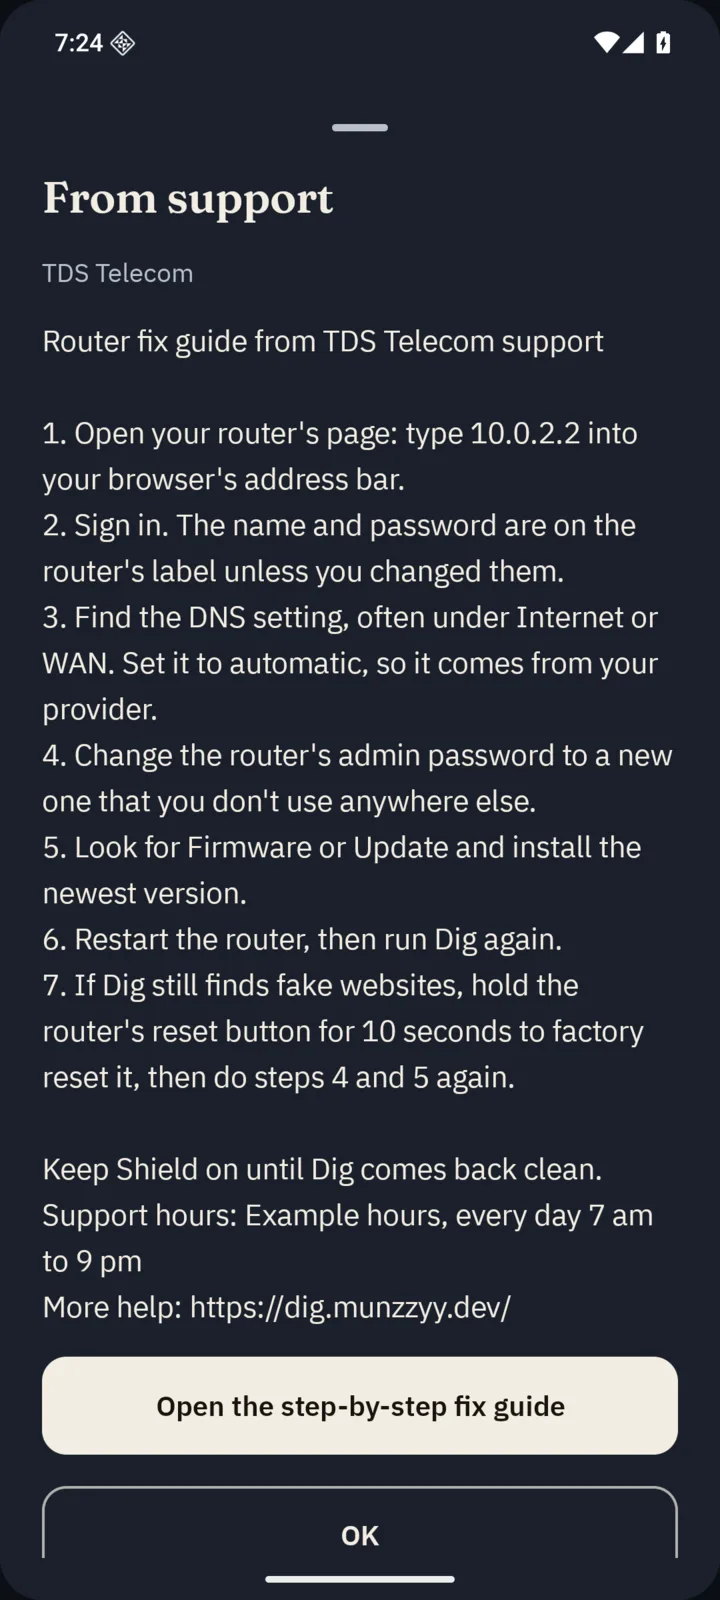
From the ticket, the agent sends the customer the router fix guide. It shows up on the phone without a tap. After the fix, the phone digs again and tells the desk. A clean dig closes the ticket as Fixed, checked from the customer's phone, and a dirty one reopens it.

For a security team, each ticket carries its MITRE ATT&CK techniques, and the desk says when a server was listed in the NCSC April 2026 advisory on APT28. Campaigns download as CSV, JSON or a STIX 2.1 bundle that passes the OASIS validator.

Three houses on the surface. A dashed line runs down from each one to the same orange dot underground, labeled 10.42.0.1, the rogue DNS server from the demo.3 homes10.42.0.1same rogue server

D / For the whole house

Owl Guard

Shield covers one phone. Owl Guard runs on the router, for the smart TV, the tablet and everything else that can't run an app. It watches the router's own DNS settings and says so within about two seconds of a change. Then it checks the router's answers with the same certificate proof and sends the desk a ticket, filed as a router. After the fix it reports again, and the desk closes that ticket.

Lock mode, off unless you ask for it, pins the router to encrypted DNS and puts a changed setting back. On OpenWrt, Guard also reads whether the router's settings page or SSH can be reached from the internet.

Guard is one small Python program for a Linux router, written to run on OpenWrt too. So far it has only run in its tests and against a stand-in router on my own PC. It hasn't run on a real router yet. For a computer there is the laptop check, one Python file with the same rules.

Guard alert / Router 1 / Demo data

This router's DNS settings were changed, and it is now sending the house to fake websites.

upstream DNS: not set became 127.0.0.1#5300

tdstelecom.com went to 10.42.0.1, which could not prove it is tdstelecom.com.

ticket sent to the support desk

On an ordinary day

Most days nobody is attacking you and the internet just isn't working. Owl is for those days too. Amber means not working. Orange is kept for a proven lie.

What's broken
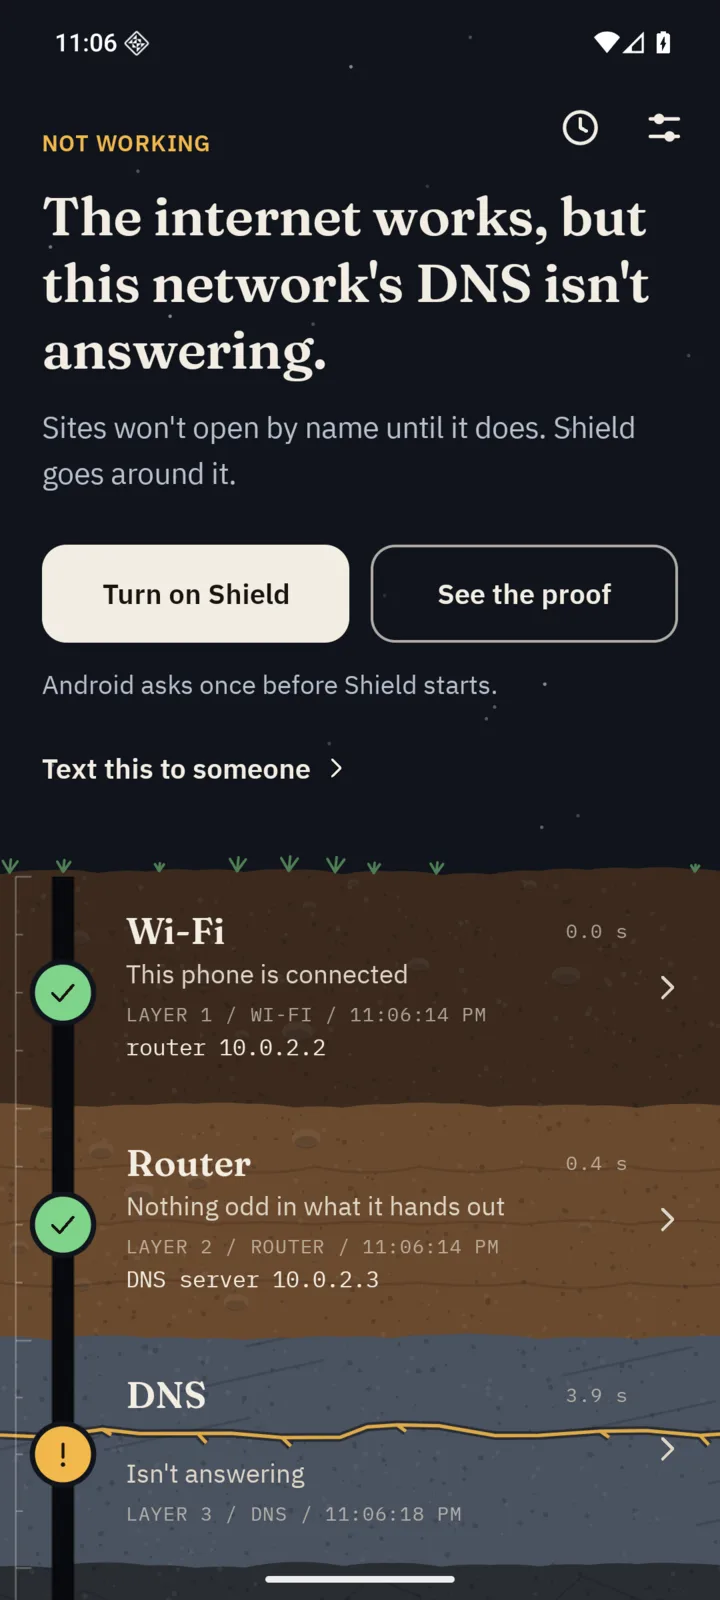
When nothing is lying, Owl says which part it is: This phone can't reach your router, Your router answers, but the internet past it doesn't, or The internet works, but this network's DNS isn't answering.
Text this to someone
Three plain lines for whoever helps you with this, shown first and then sent through the phone's own share sheet. Owl asks for no contacts.
One word on a new Wi-Fi
Switch it on and a new network gets one word: Honest, Sign in first, Lying or Can't tell. Honest means it gave real addresses for the sites Owl checked. It doesn't mean nobody is watching.
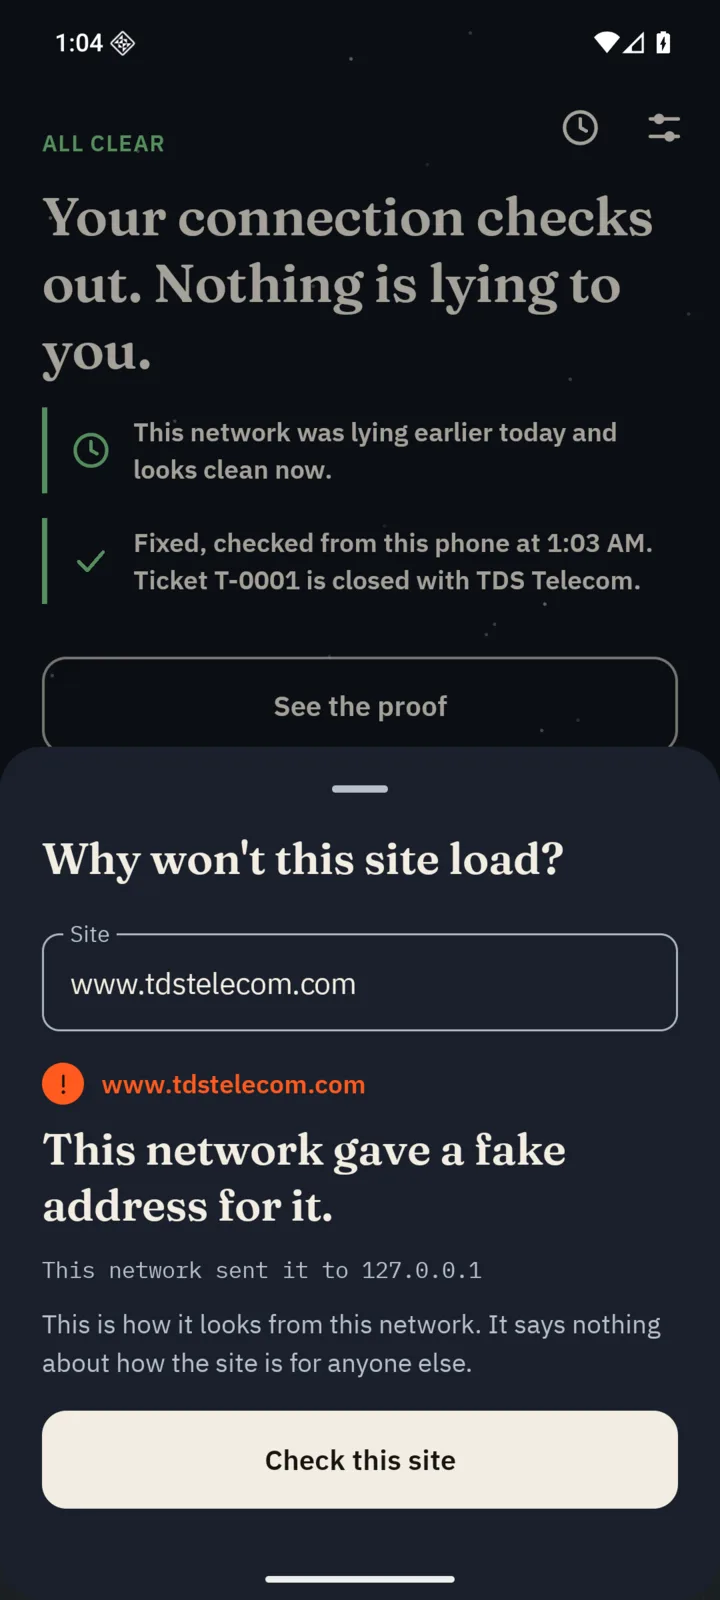
Why won't this site load?
Type a name or share a link. Owl says if this network blocks it, gave a fake address for it, or the site isn't answering from here.
What to change now
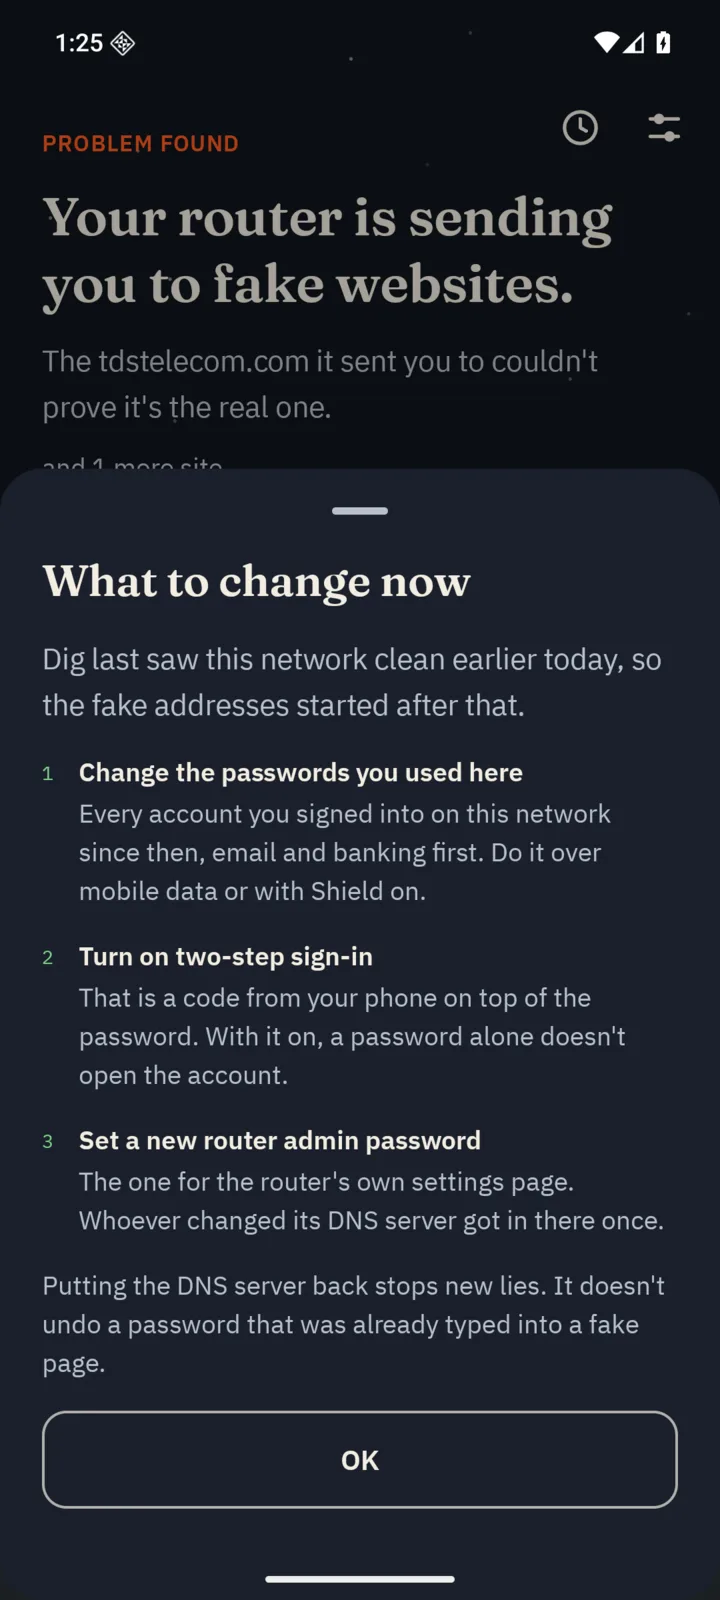
After a proven lie: which passwords to change, counted from the last clean dig. Fixing the router doesn't undo a password already typed into a fake page.
Shield's receipt
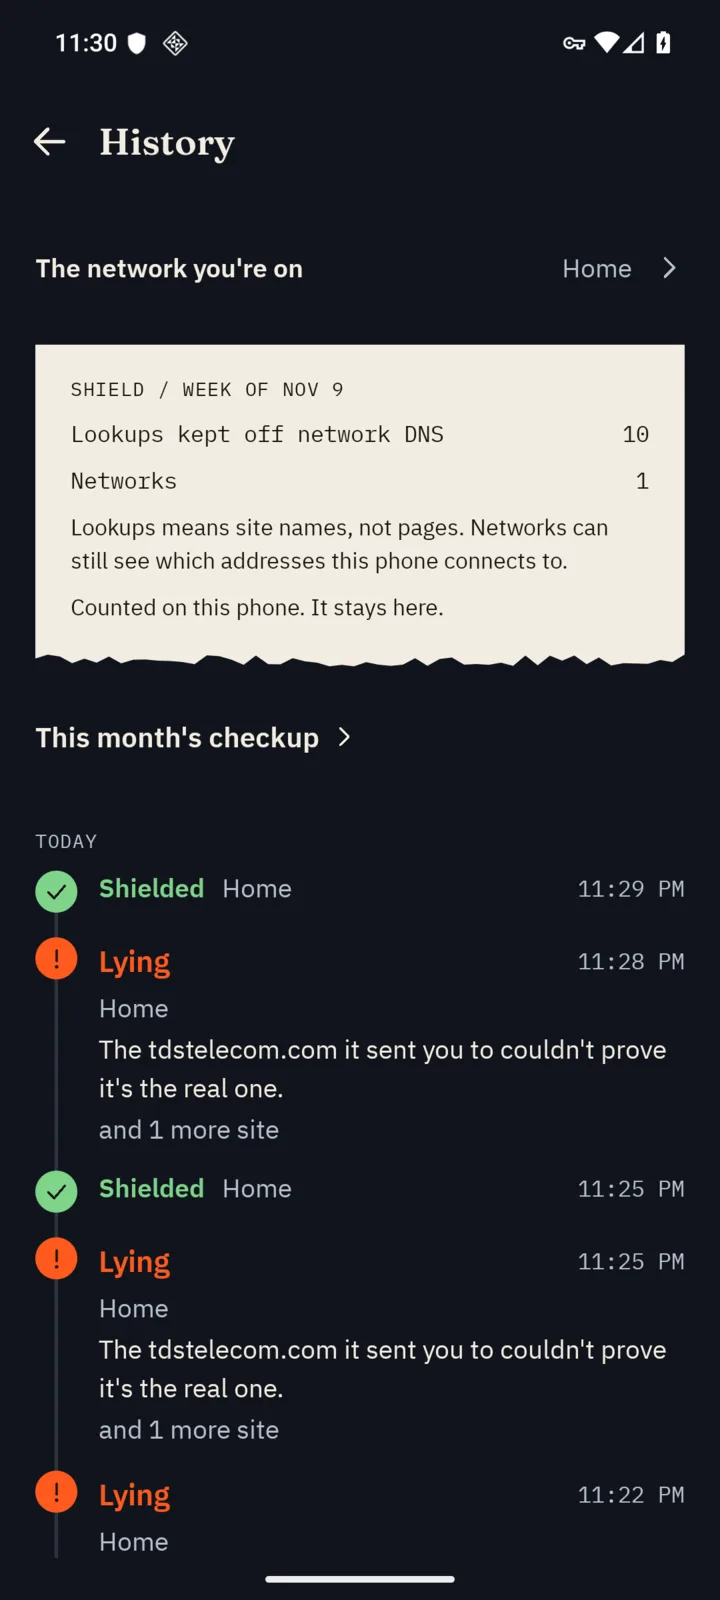
Once a week, how many lookups Shield kept off how many networks' DNS. Counted on the phone, and it stays there.

What else a dig looks at

The main check can say fake. These can't. They warn or leave a note.

54 names, mostly sign-in pages
Every dig checks Microsoft, Outlook, Google, Apple, banks, email and tax sign-in pages. Those are the kind of name the April attackers lied about.
IPv6 answers
Compared by the same rule. A bad one is a warning for now, because I could not measure that path from a desk with no IPv6.
A second opinion
When a Wi-Fi blocks encrypted DNS, Owl asks before checking the same sites over mobile data, and says which network each answer came from.
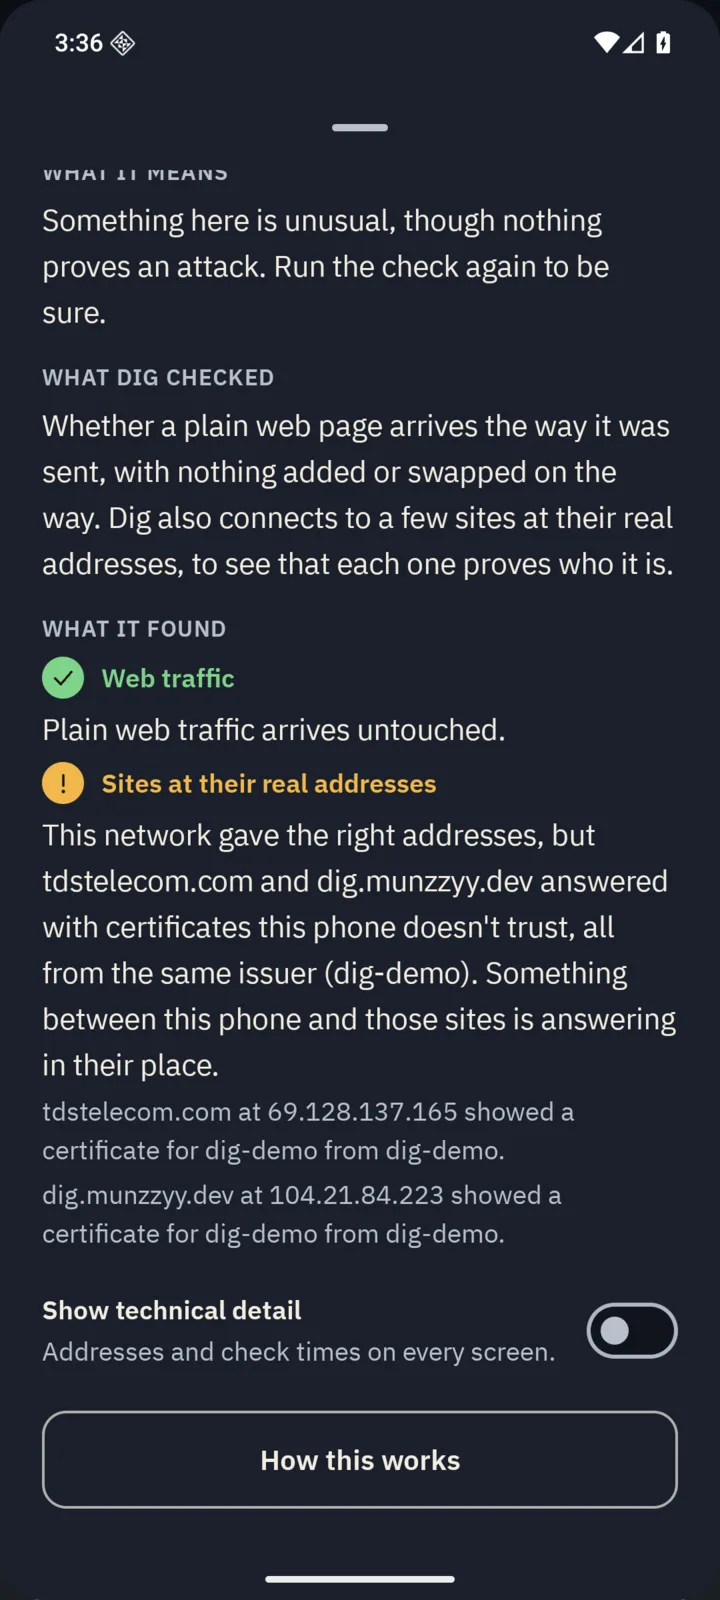
At the real addresses
When the answers agree, Owl still connects to three of the sites. Two of them answering with certificates from the same untrusted issuer means something in between is answering for them.
Made-up names
Owl asks the Wi-Fi for names that can't exist. A device that answers two of them is spoofing names, which is how some tools collect sign-ins on shared Wi-Fi.
Read this sign-in page
On hotel or cafe Wi-Fi, Owl reads the sign-in page without typing anything and says what it asks for and where it sends it. Facts only.
Changed terms
Owl says when a network that used to ask for a password stops asking, or adds a proxy.
Caught DNS
Some networks answer DNS that was meant for Cloudflare or Google. Owl asks both a question only they answer their own way, and warns when something else did.
The NCSC list
Owl carries the 182 server addresses from the NCSC advisory3 and matches them on the phone. A match reads This server was listed in the NCSC's April 2026 advisory on APT28. If the router's own page names a model from that advisory, Owl says the model is named there, and never more.
Your provider's servers
A paired desk hands the phone the provider's DNS servers, so Owl can say whether the router's is one of them.
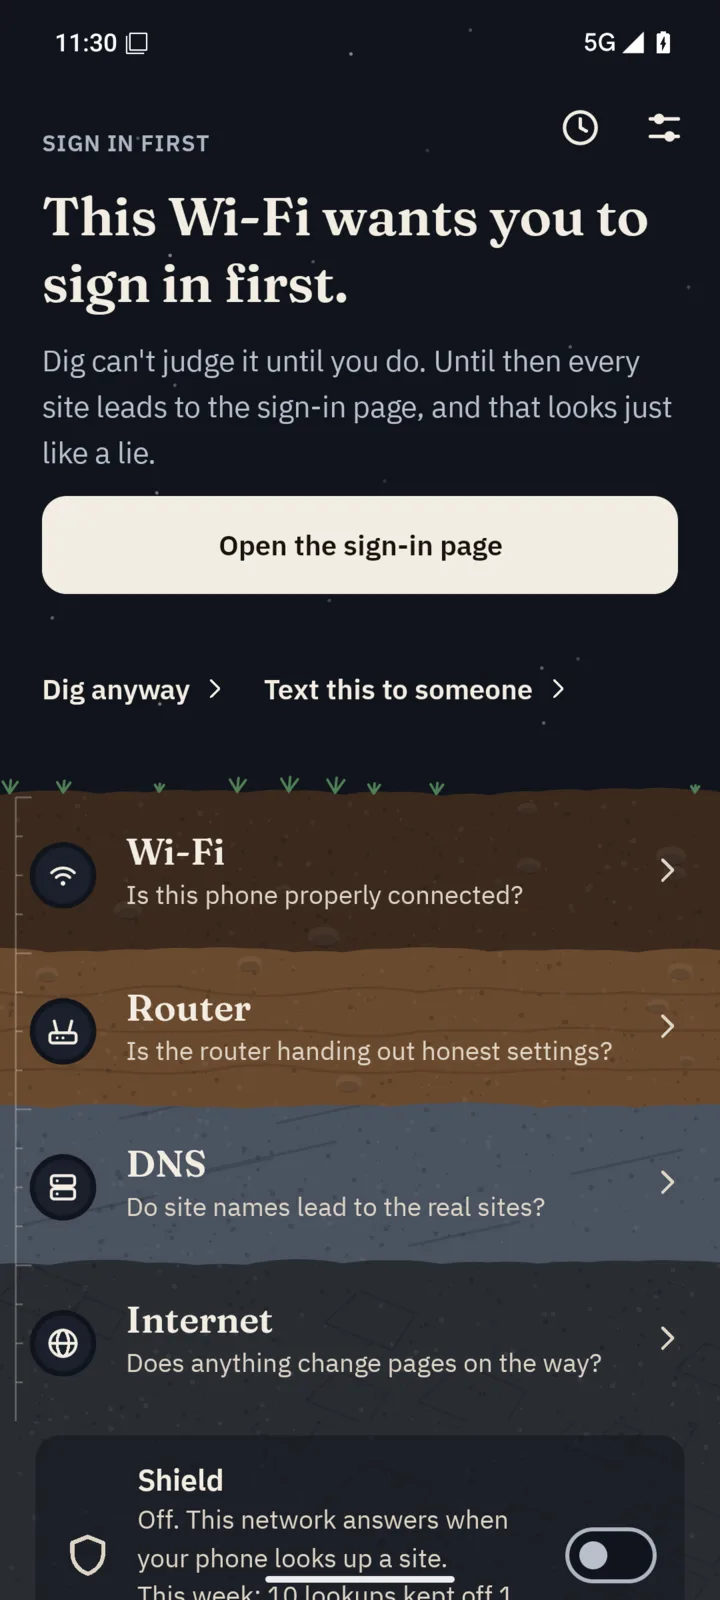
Sign in first
On Wi-Fi with a sign-in page, Owl holds and says so. Before you sign in, every site looks like a lie.
The phone's clock
More than five minutes off, and Owl says so, because that breaks secure sites.
Added authorities
Owl lists certificate authorities somebody added to the phone. Owl doesn't trust them. Your browser does.
A different box
Owl says when a different device starts handing out addresses on a network it has seen before.
Router doors
It tries the router's telnet port from inside the home, and warns if it answers.
Notes in the detail view
Added November 15: a certificate with no transparency record, two answers to one lookup, a page changed on its way to the phone, and one wrong certificate at several sites. They never change a verdict.
Who it's for

Nobody on this list uses Owl yet. It is a weekend build. This is who each part was made for.

A person at home
One button that says which part is broken: the Wi-Fi, the router or the line past it. When the network lied, the proof and what to change.
Someone on public Wi-Fi
One word about the network before you sign in to anything, a plain reading of its sign-in page, and Shield while you're there.
A family helper
Text this to someone sends you three plain lines, so nobody reads a screen out over the phone. A parent can mark the network as one someone else runs.
A small business
The laptop check is one file with nothing to install. Guard watches the office router and can put a changed setting back.
A company IT team
People working from home send sealed tickets to the company's own desk. Several home routers pointing at one rogue server show up as one campaign, with ATT&CK tags and a STIX 2.1 export.
An ISP support desk
The customer arrives with the diagnosis and the proof. The agent sends the fix guide, and a clean second dig closes the ticket as fixed. The desk's name and wording come from one config file.

Sample 04 / Screens / From the build

What it looks like

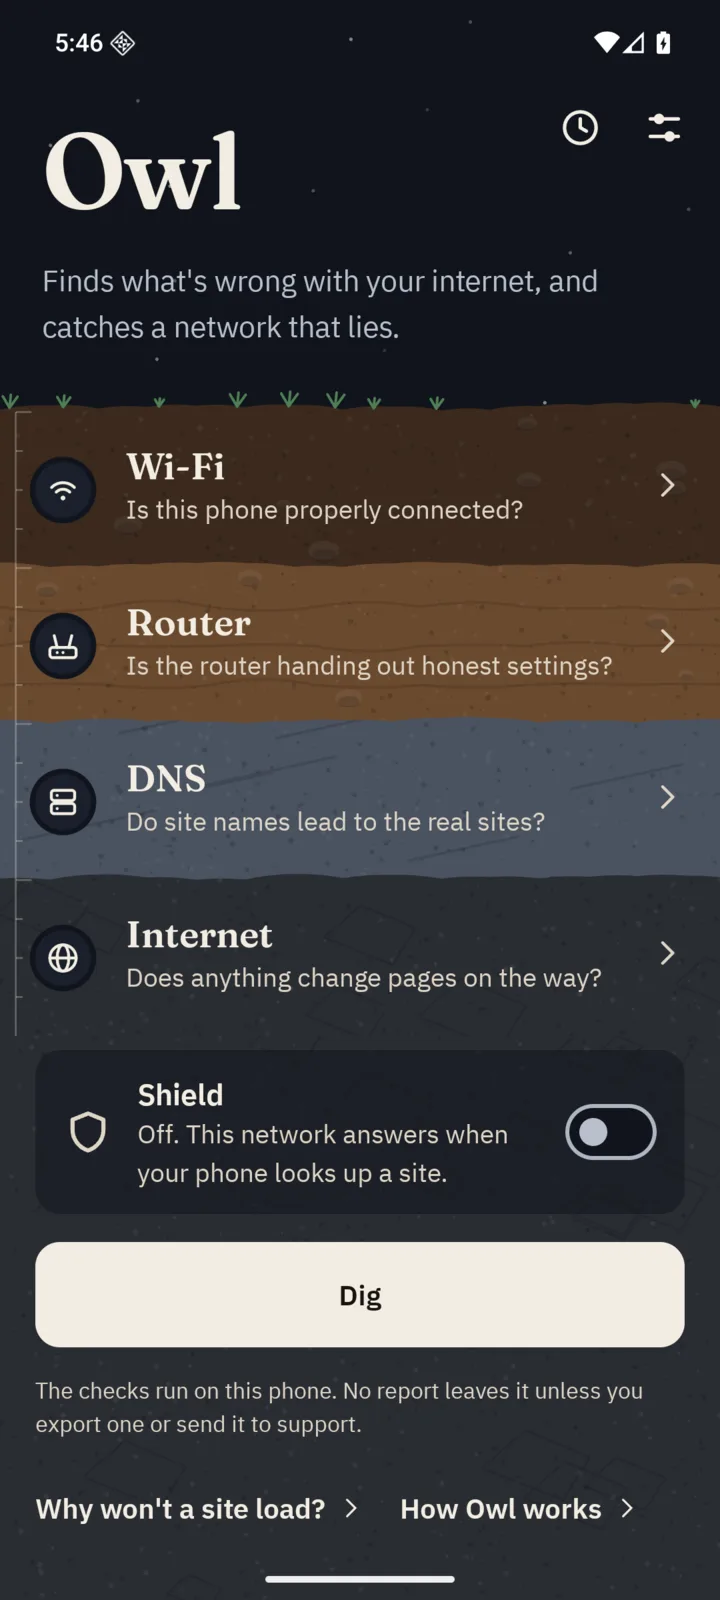
  • Owl's main screen. Under the name: Finds what's wrong with your internet, and catches a network that lies. Four earth layers, each with a question, the Shield switch, a Dig button and a link that reads Why won't a site load.
    Main screenThe main screen. Each layer asks its question, and there is one button.
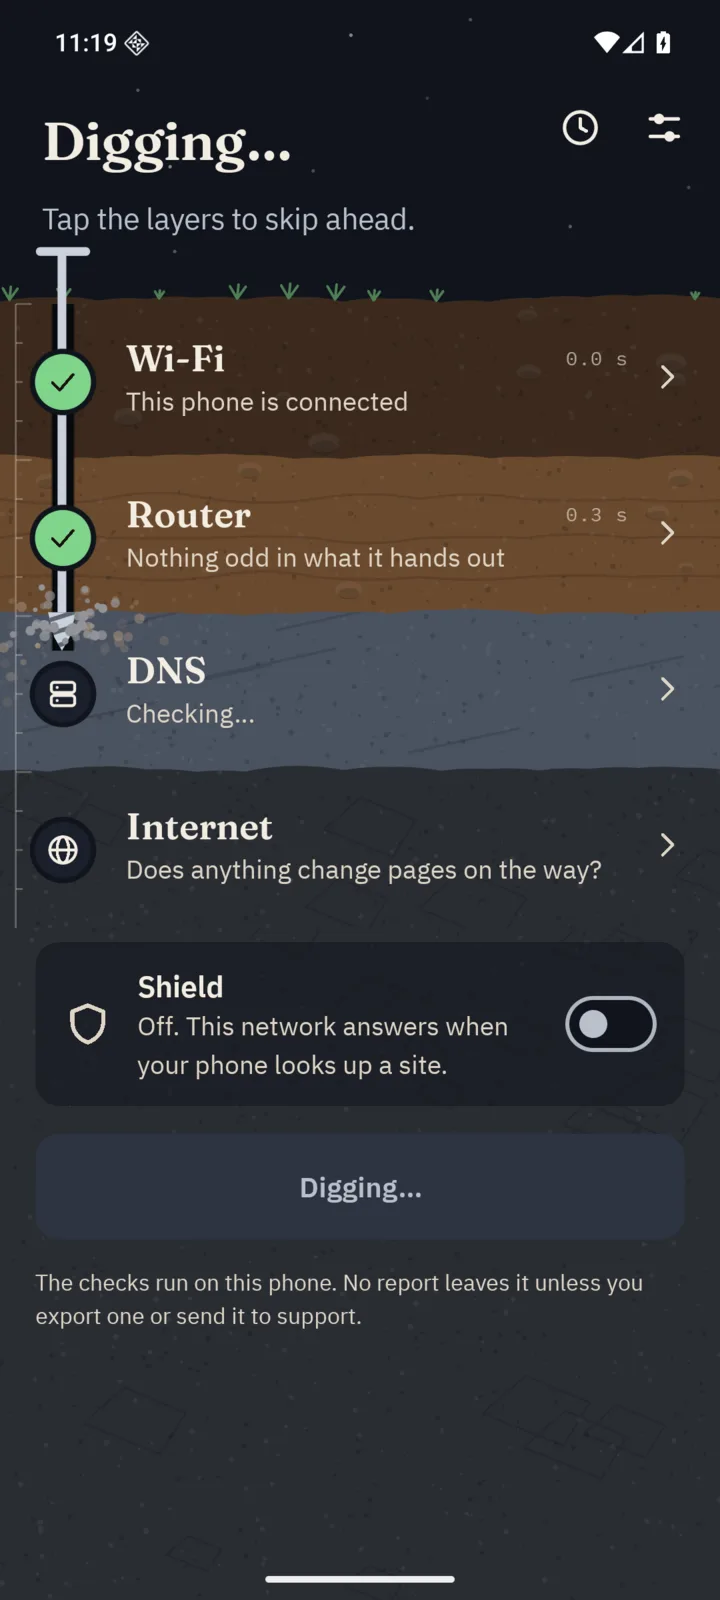
  • Owl in the middle of a run, with the drill partway down the layers.
    DiggingThe drill passes each layer as its check finishes.
  • Owl's verdict in amber: Not working. The internet works, but this network's DNS isn't answering. Wi-Fi and Router have green checks and the DNS layer has an amber mark and reads Isn't answering.
    What's brokenNothing is lying here. The DNS just isn't answering, and Owl says which part that is. Staged on an emulator by dropping its DNS traffic, with technical detail switched on.
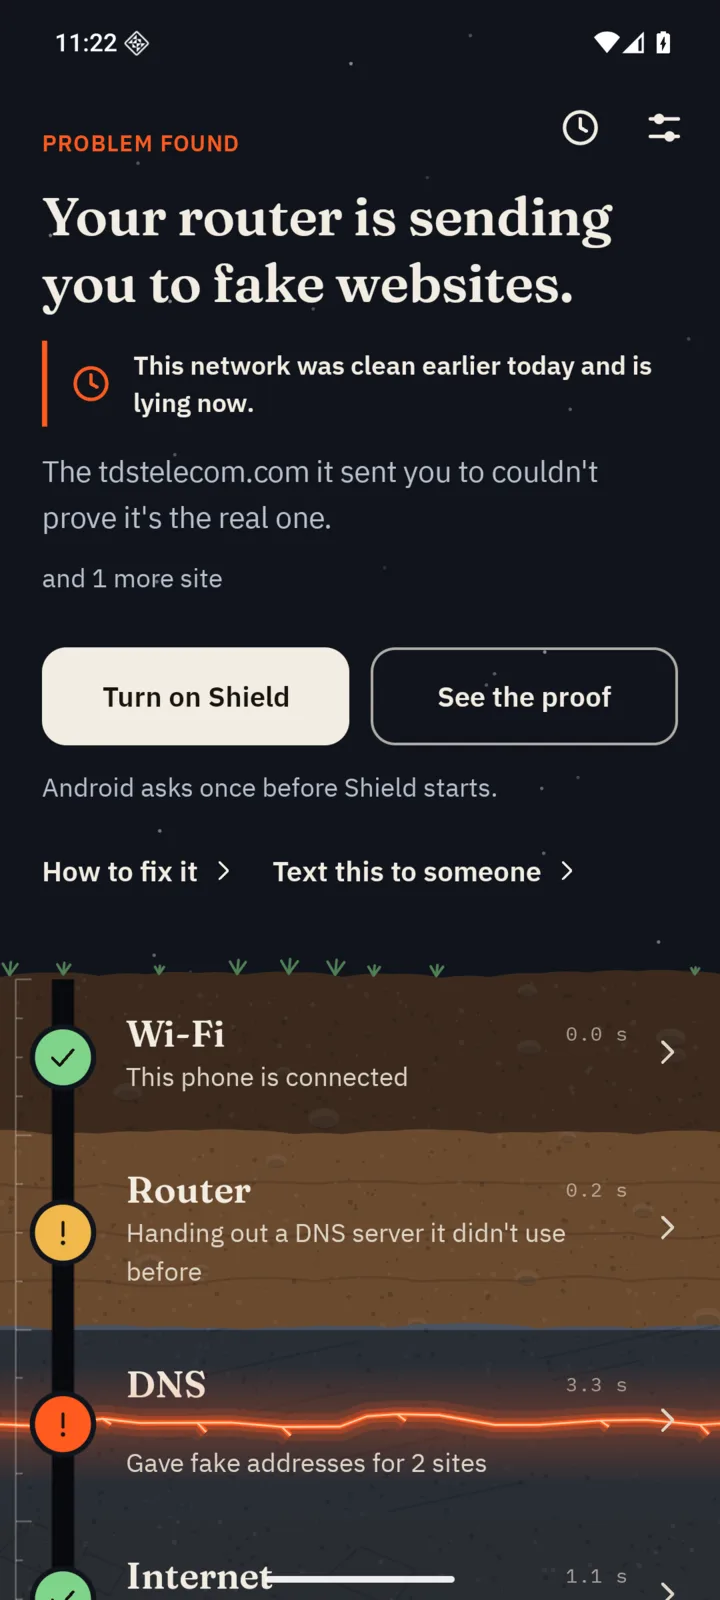
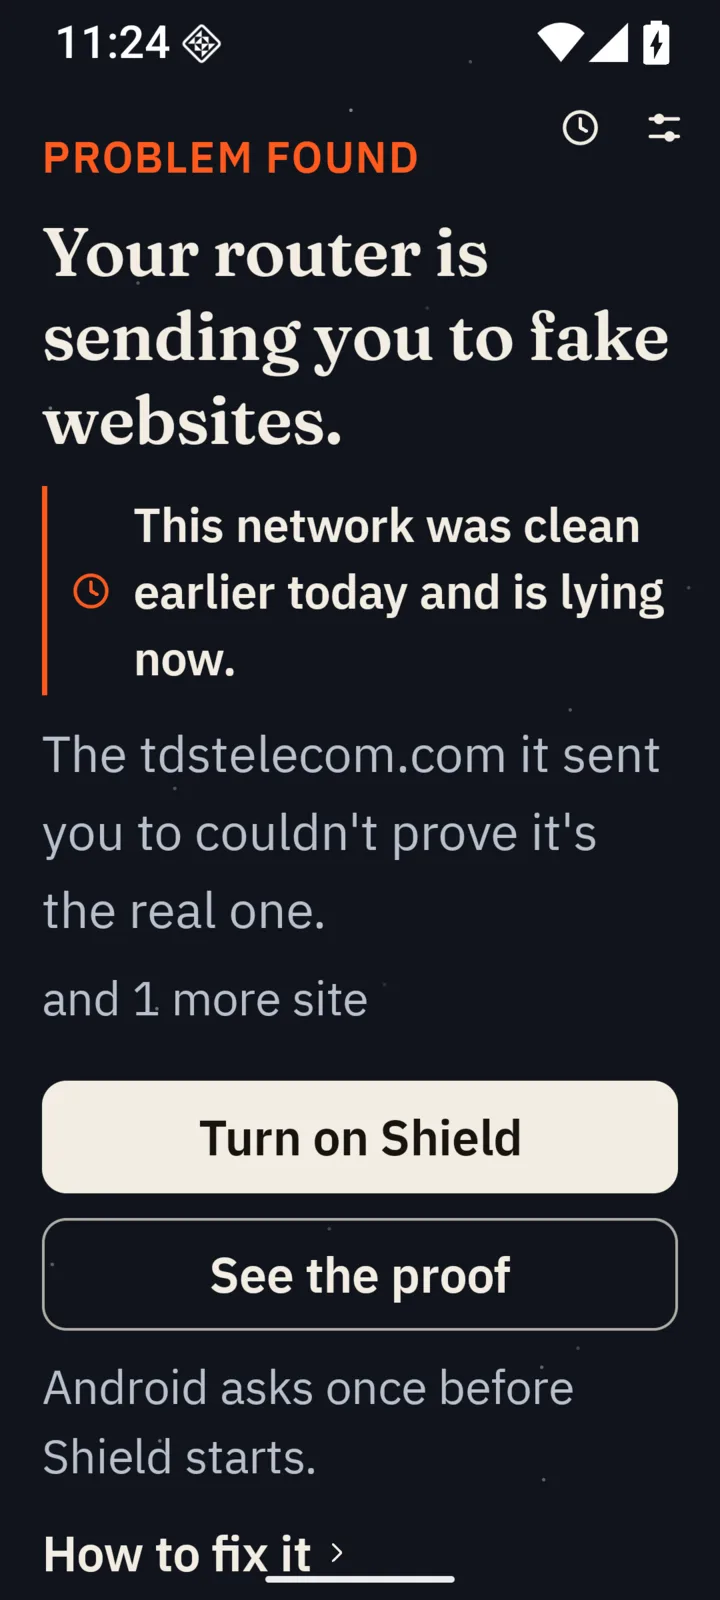
  • Owl after finding a hijack. Problem found: your router is sending you to fake websites. A note says the network was clean earlier today and is lying now. The Router layer is amber and the DNS layer is cracked and orange.
    A lie, provenThe DNS layer cracks. The router goes amber, because it handed out the server that lied.
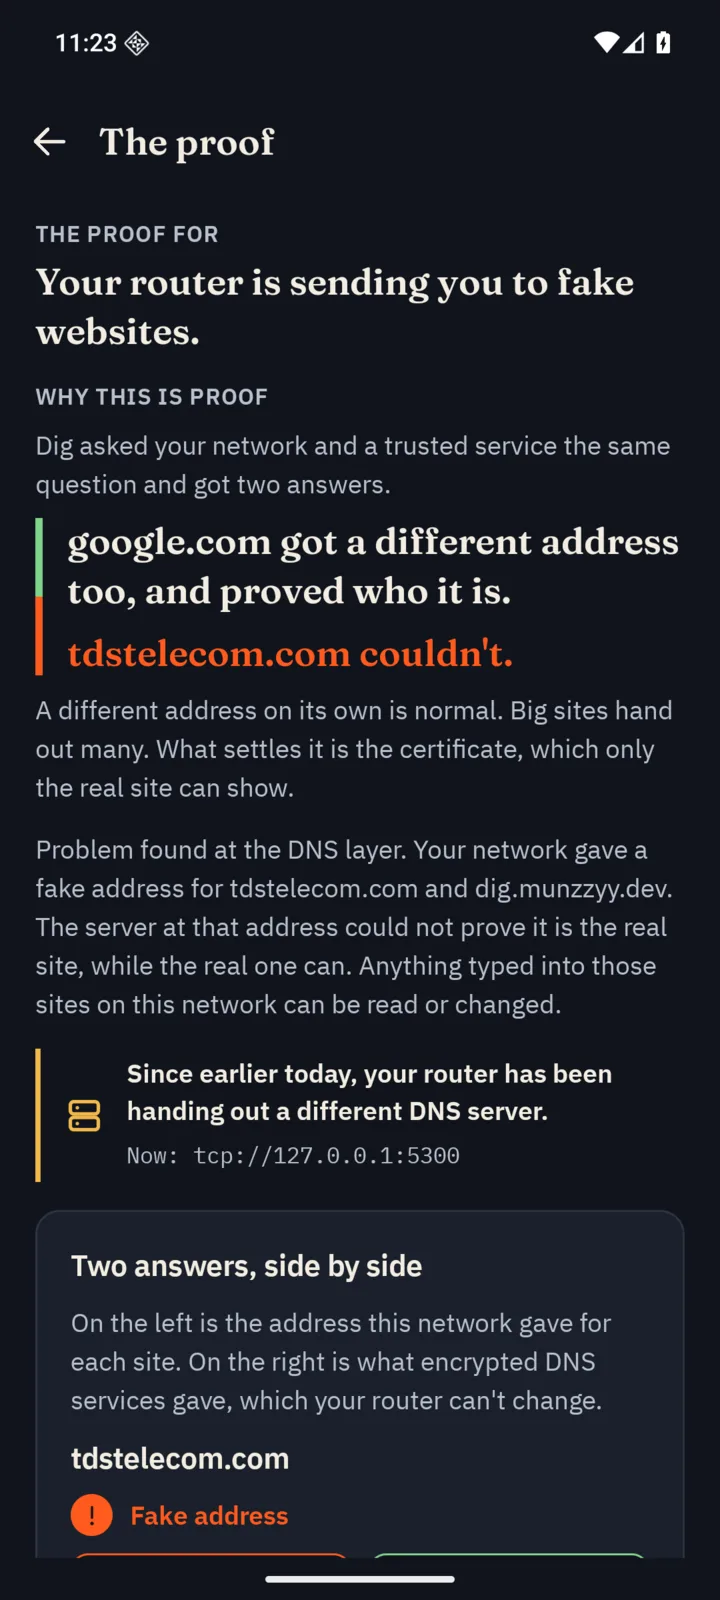
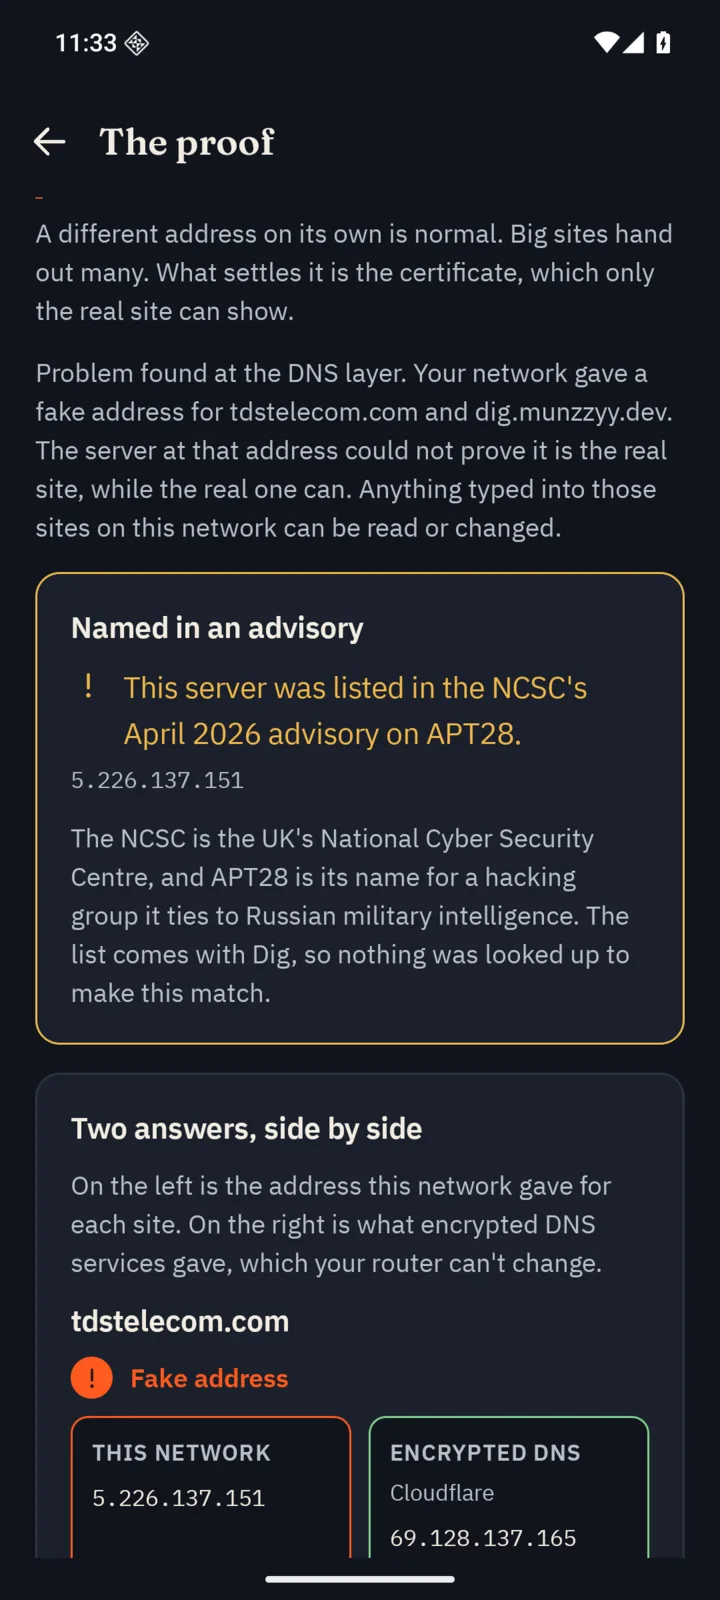
  • The proof screen. google.com got a different address too, and proved who it is. tdstelecom.com couldn't.
    The proofWhat the network said next to what encrypted DNS said, and the certificate that failed.
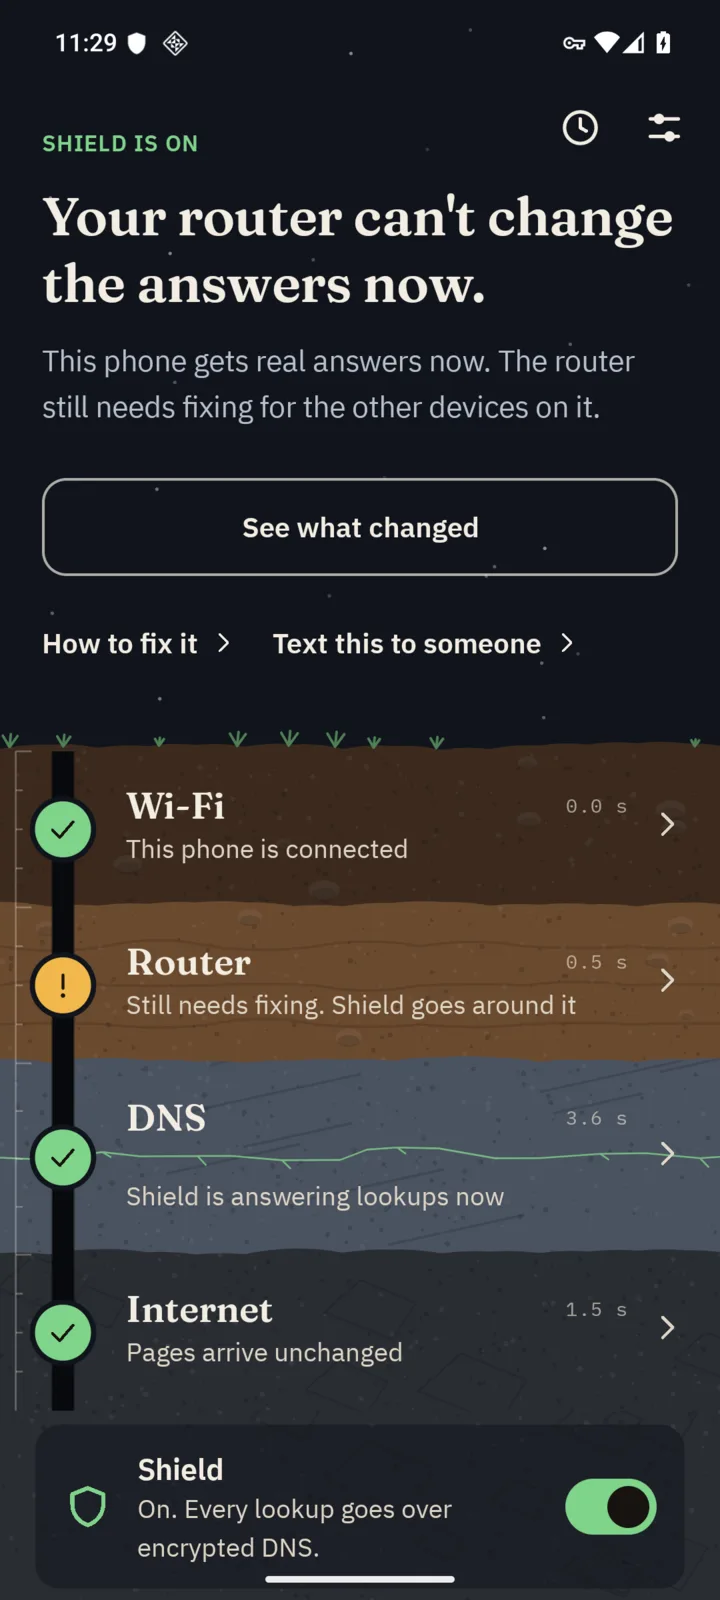
  • Owl with Shield on: your router can't change the answers now. The DNS layer has a green check and the Router layer reads Still needs fixing, Shield goes around it.
    Shield onWith Shield on the DNS layer heals. The router stays amber until it is fixed.
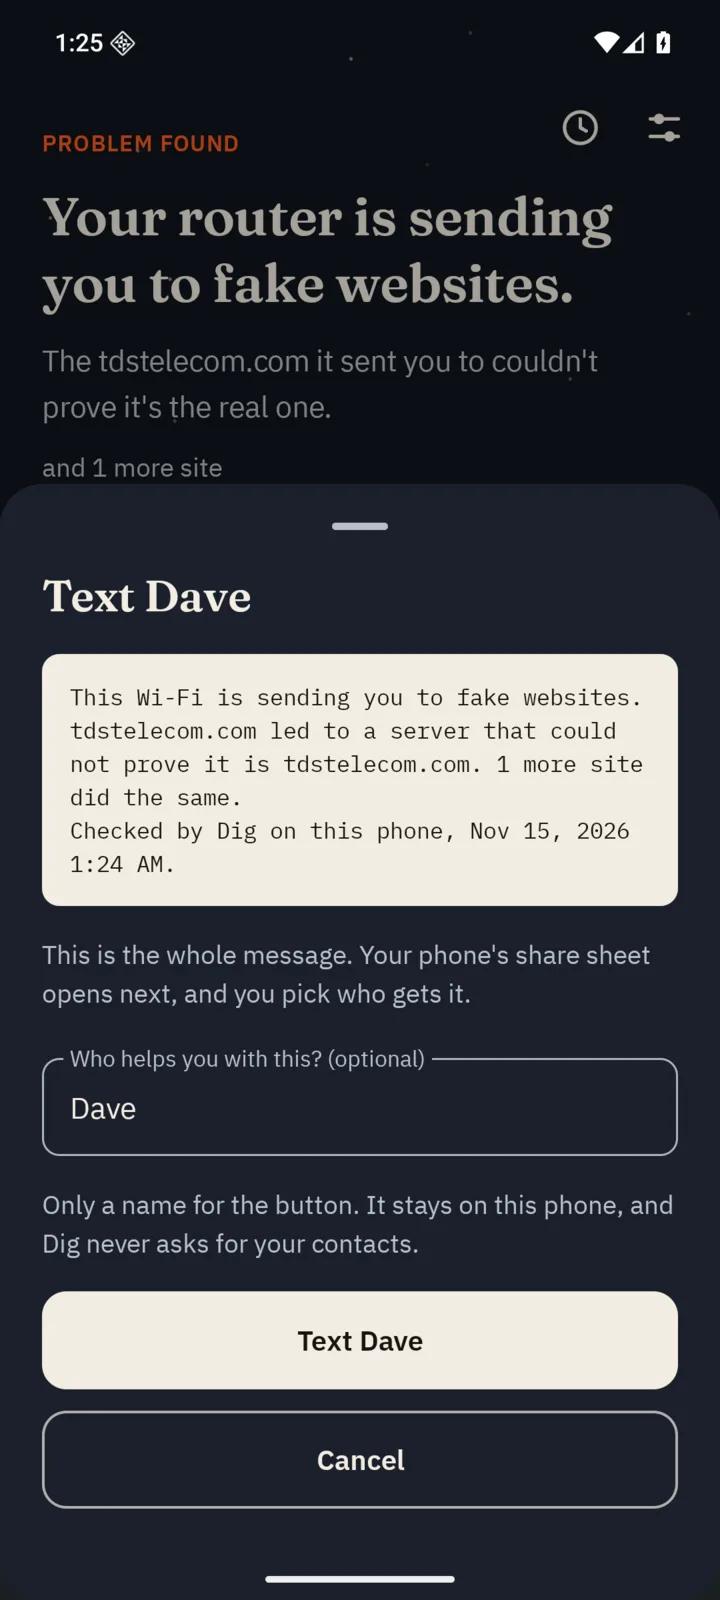
  • A sheet titled Text Dave with the exact message in a cream box: this Wi-Fi is sending you to fake websites, the site that could not prove itself, and when Owl checked. Below it, a box for the helper's name and a Text Dave button.
    Text this to someoneThree plain lines for whoever helps you with this. It goes through the phone's own share sheet.
  • A sheet titled What to change now with three steps: change the passwords you used here, turn on two-step sign-in, and set a new router admin password.
    What to change nowAfter a proven lie: which passwords to change, counted from the last clean dig in History.
  • A sheet titled Why won't this site load, with www.tdstelecom.com in the box and the answer: this network gave a fake address for it.
    Why won't this site load?Type a name or share a link, and Owl checks that one site from this network.
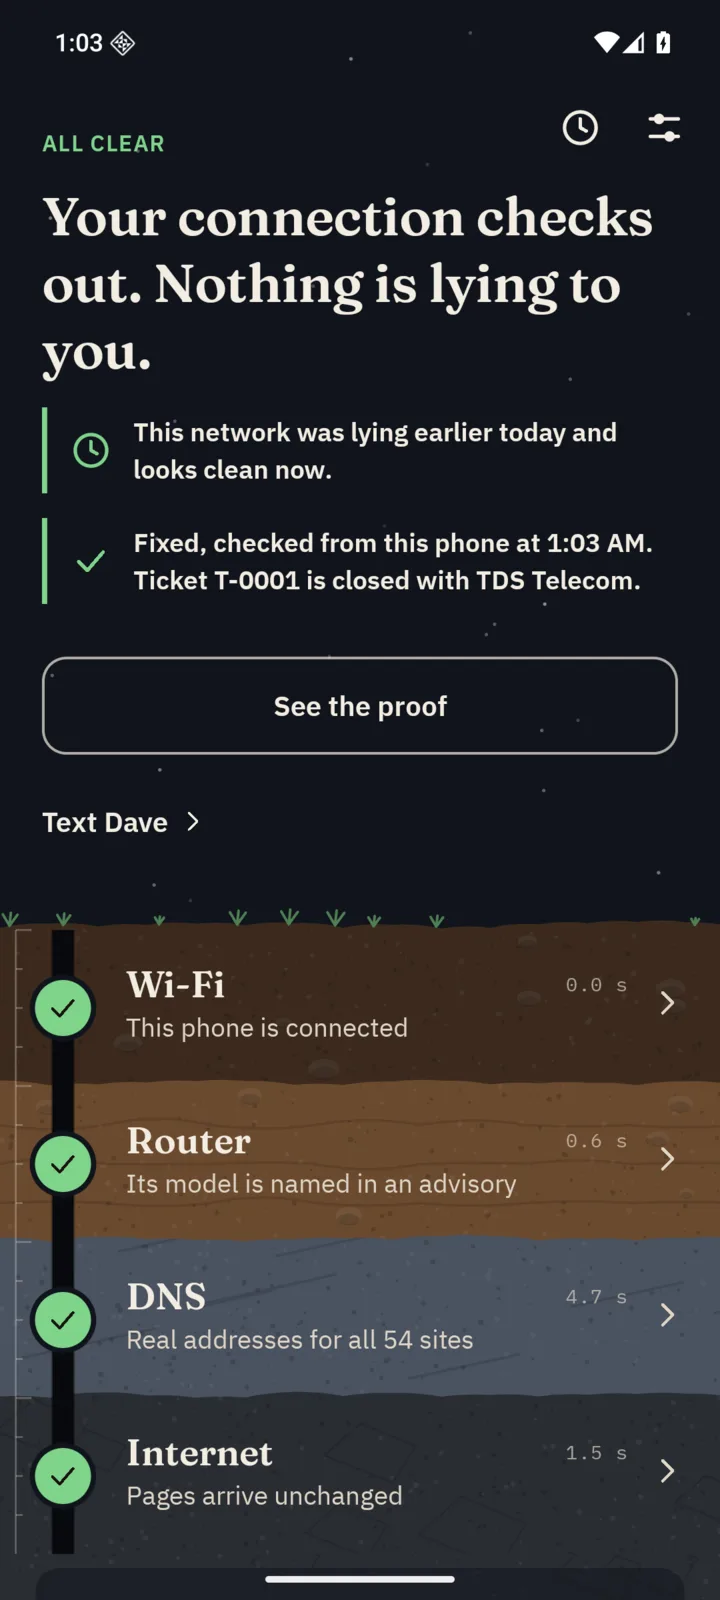
  • Owl's all clear screen with two notes: this network was lying earlier today and looks clean now, and Fixed, checked from this phone at 1:03 AM, ticket T-0001 is closed with TDS Telecom.
    Fixed, with proofAfter the fix, a clean dig closes the ticket on the desk.
  • The history screen. A paper slip counts lookups kept off network DNS this week. Below it, digs by day, marked Shielded or Lying.
    HistoryPast digs by day, lies listed in full, and Shield's receipt for the week as a paper slip.
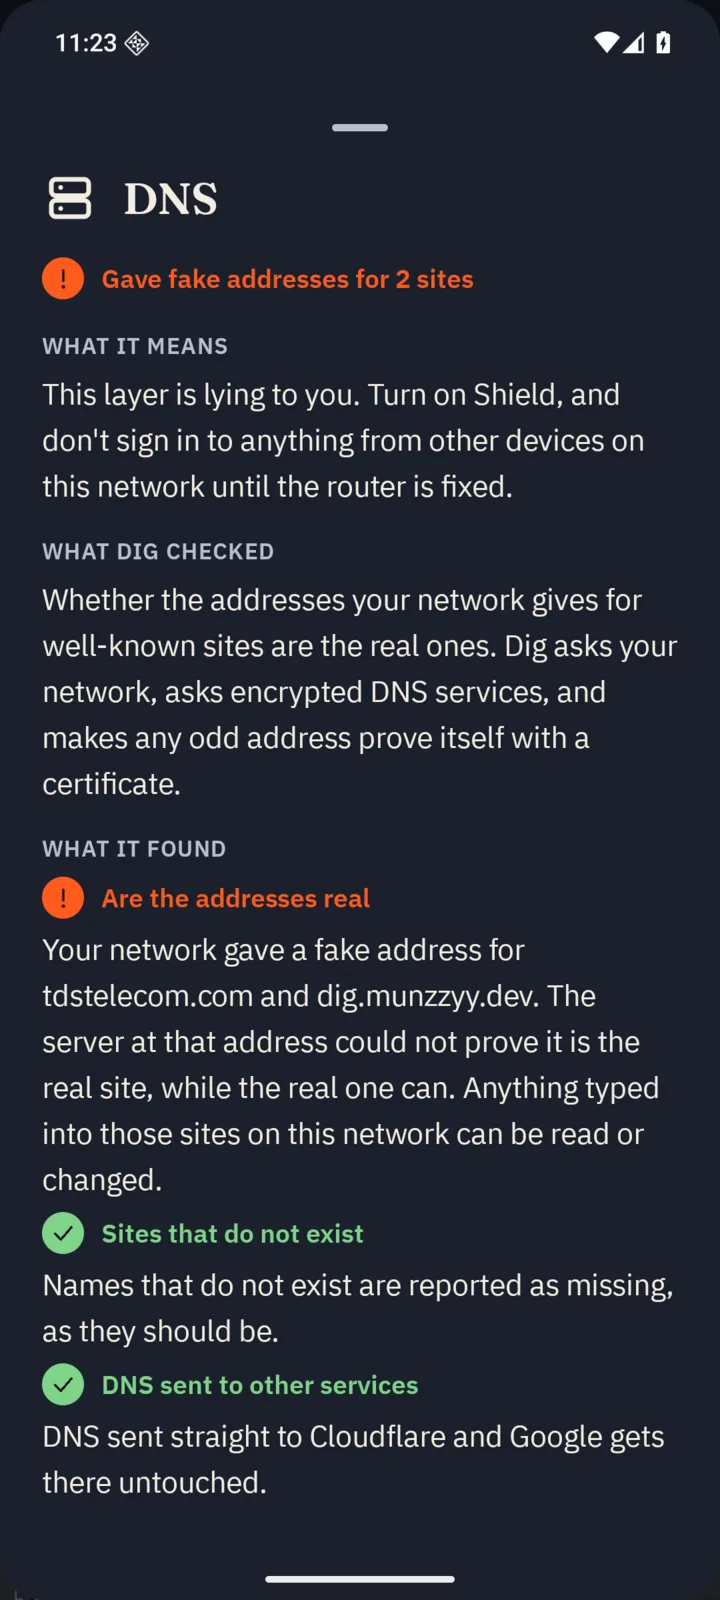
  • The DNS layer sheet after a hijack: gave fake addresses for 2 sites, what it means, what Owl checked and what it found.
    Inside a layerTap a layer to see what it means, what was checked and what was found.
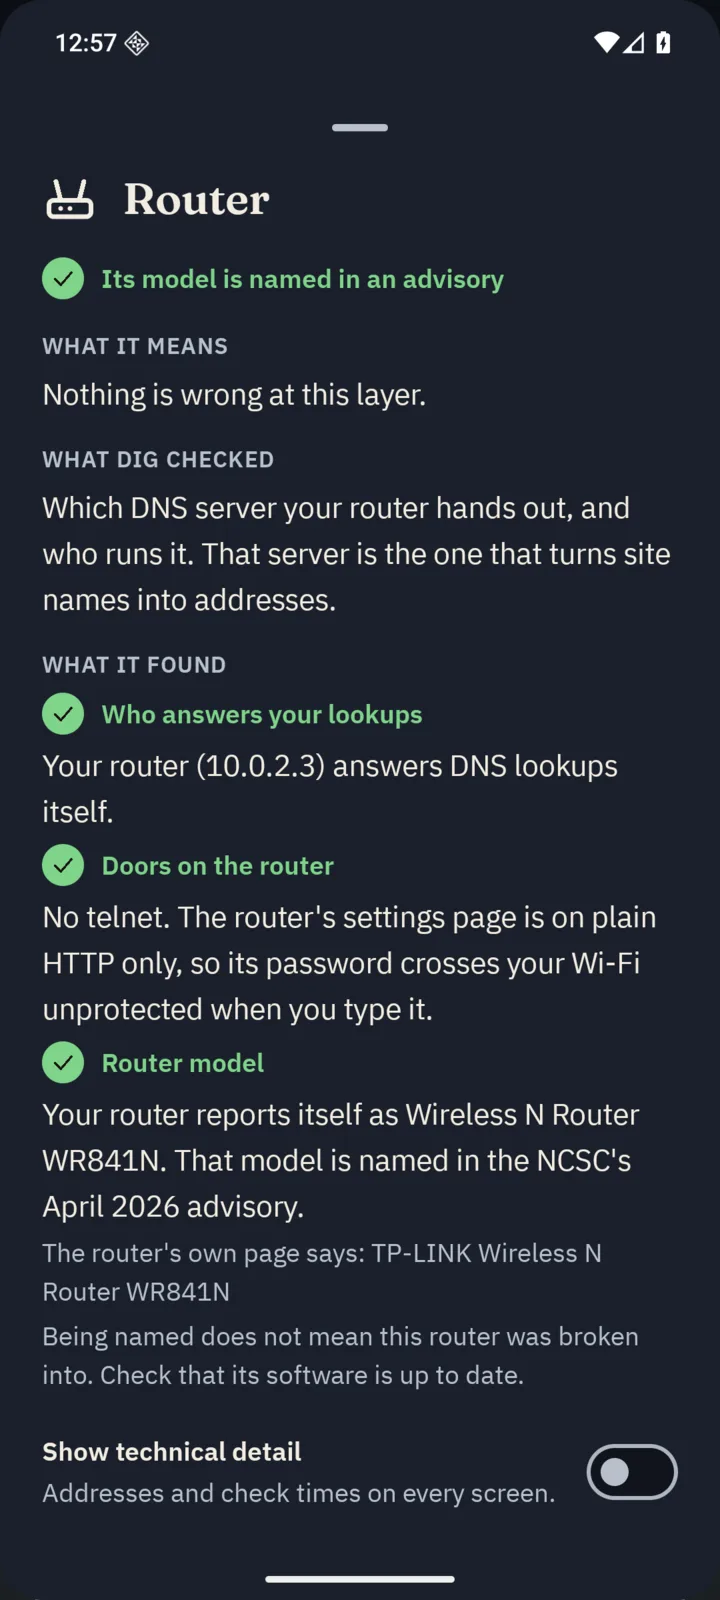
  • The Router layer sheet with a line that reads: your router reports itself as Wireless N Router WR841N. That model is named in the NCSC's April 2026 advisory. Being named does not mean this router was broken into.
    Router modelThe router's own page named a model that the NCSC advisory lists. Staged with the demo kit answering as that model.
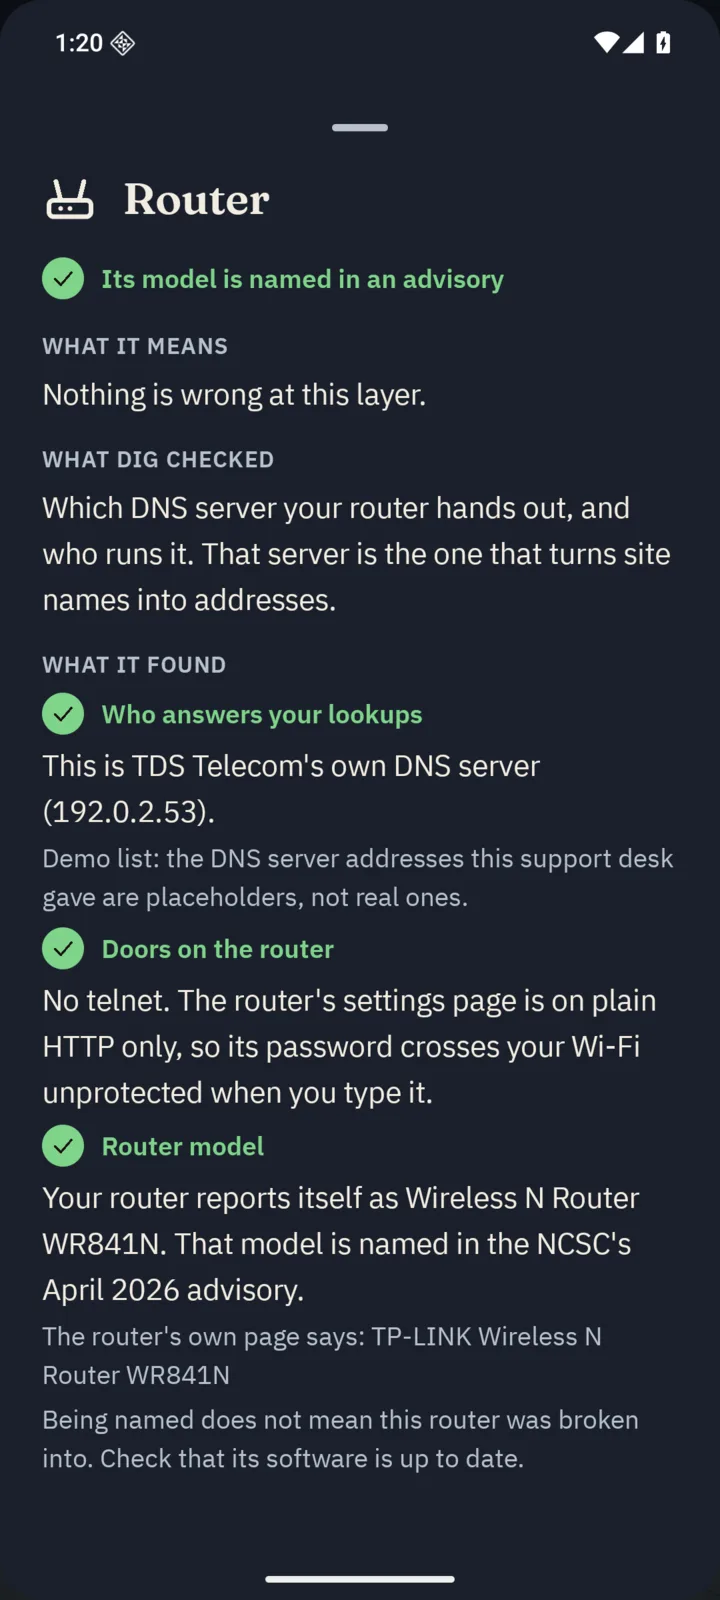
  • The Router layer sheet with a line that reads: this is TDS Telecom's own DNS server, 192.0.2.53, and a note that the list is a demo list of placeholders.
    Your provider's serversA paired desk hands the phone its list of DNS servers. These are placeholder addresses, and the screen says so.
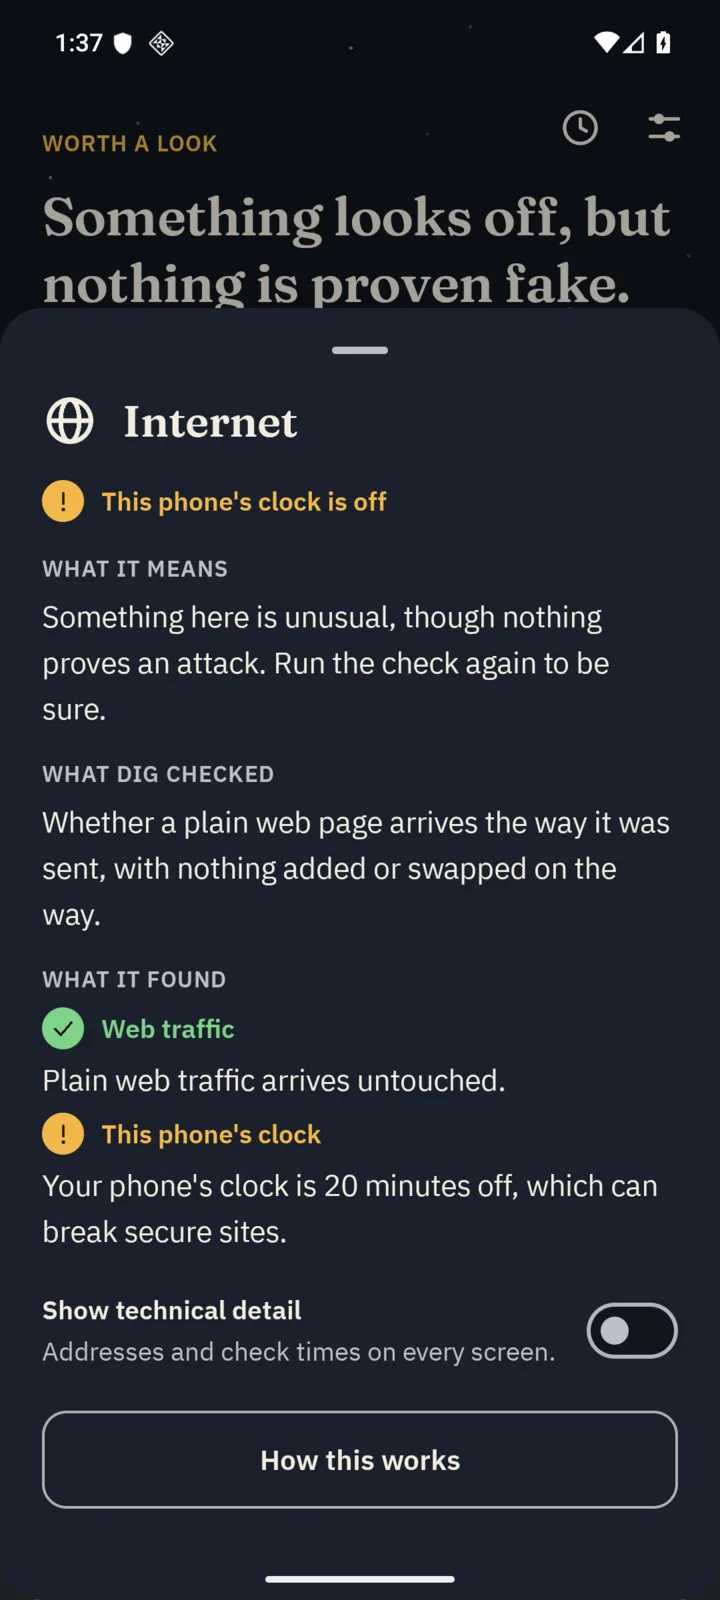
  • The Internet layer sheet with an amber line: your phone's clock is 20 minutes off, which can break secure sites.
    Phone clockA clock that is off breaks secure sites. Staged by setting the emulator's clock ahead.
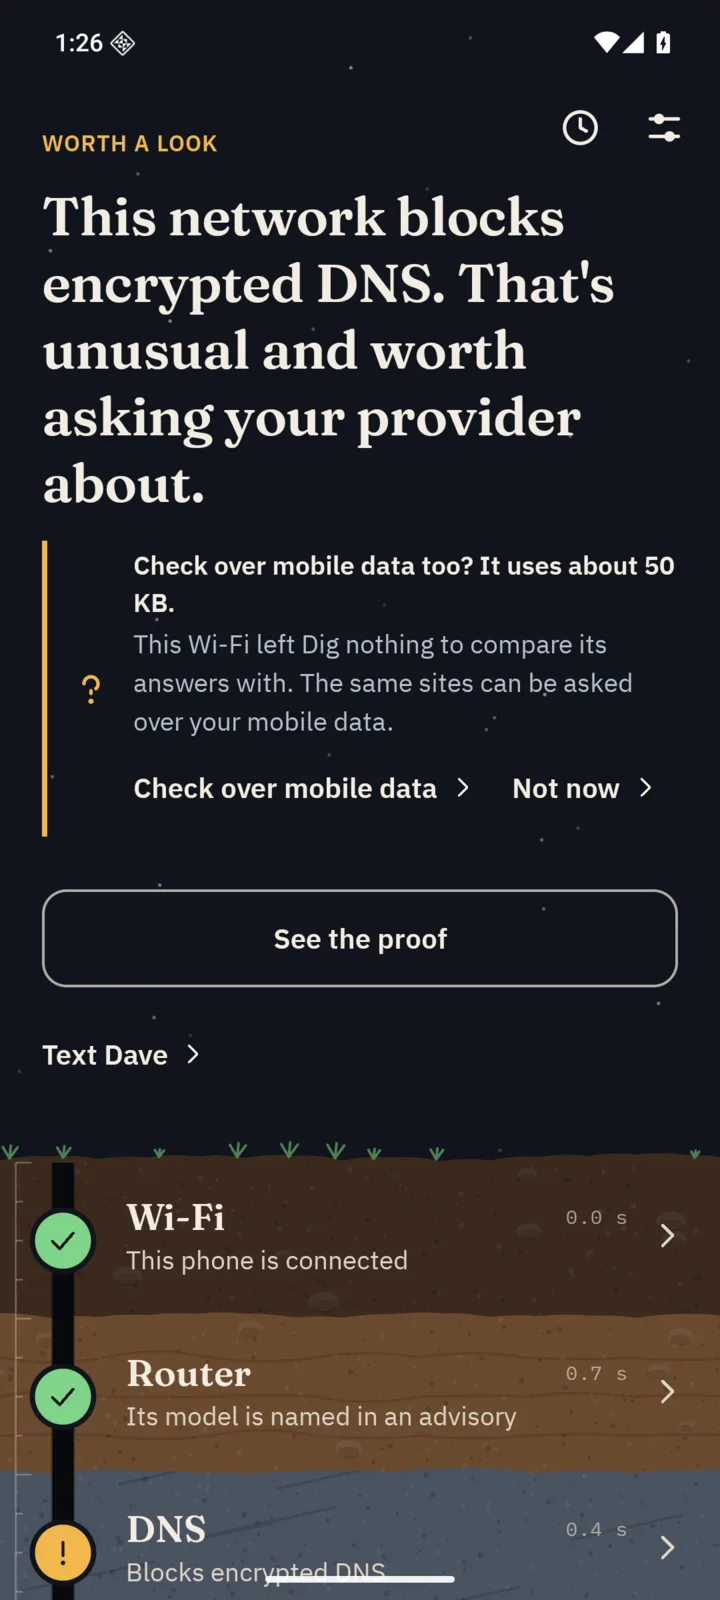
  • Owl saying this network blocks encrypted DNS, with a question under it: check over mobile data too? It uses about 50 KB.
    A second opinionWhen a Wi-Fi blocks encrypted DNS, Owl asks before checking the same sites over mobile data.
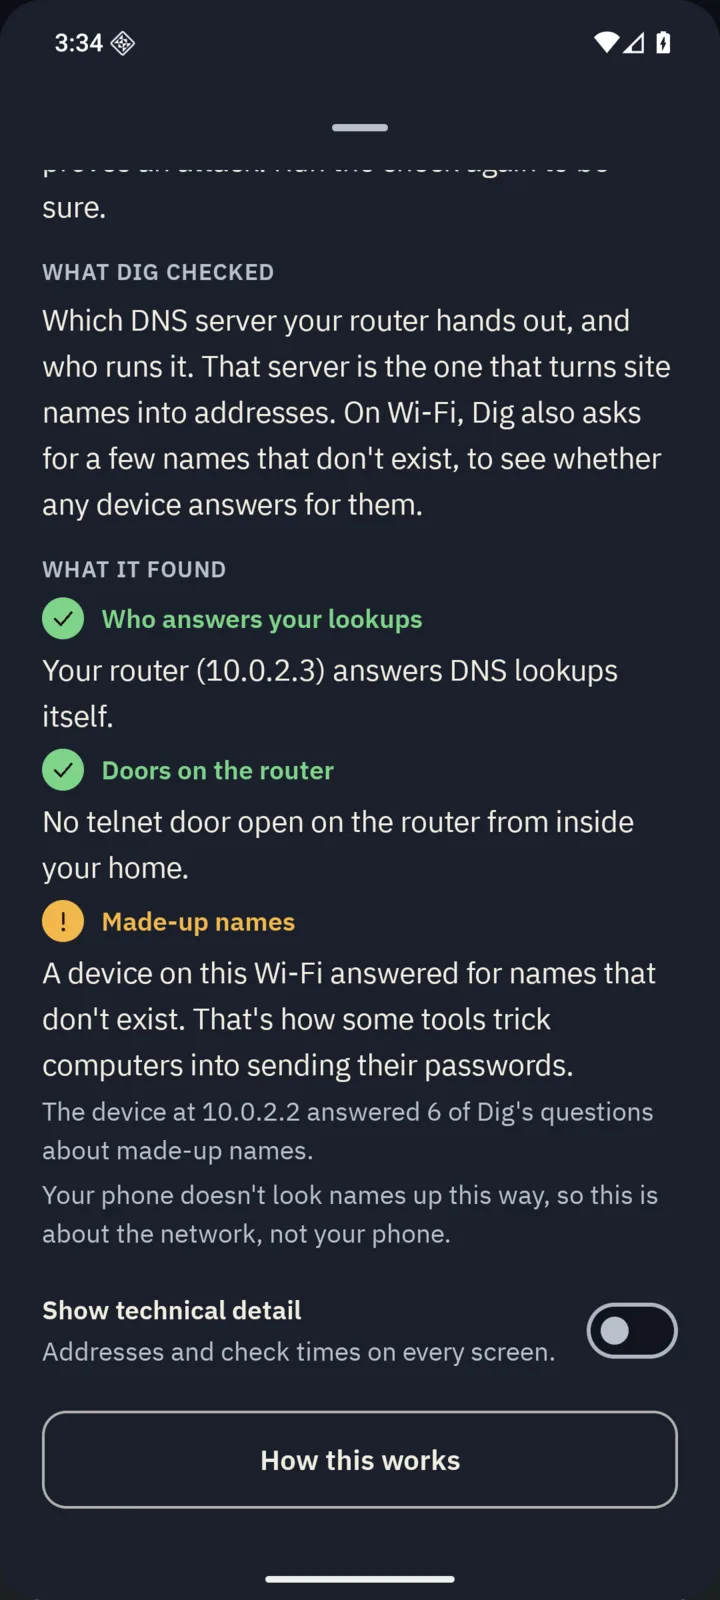
  • The Router layer sheet with an amber line: a device on this Wi-Fi answered for names that don't exist. That's how some tools trick computers into sending their passwords.
    Made-up namesOwl asks the Wi-Fi for names that can't exist. Here the demo kit answered for them.
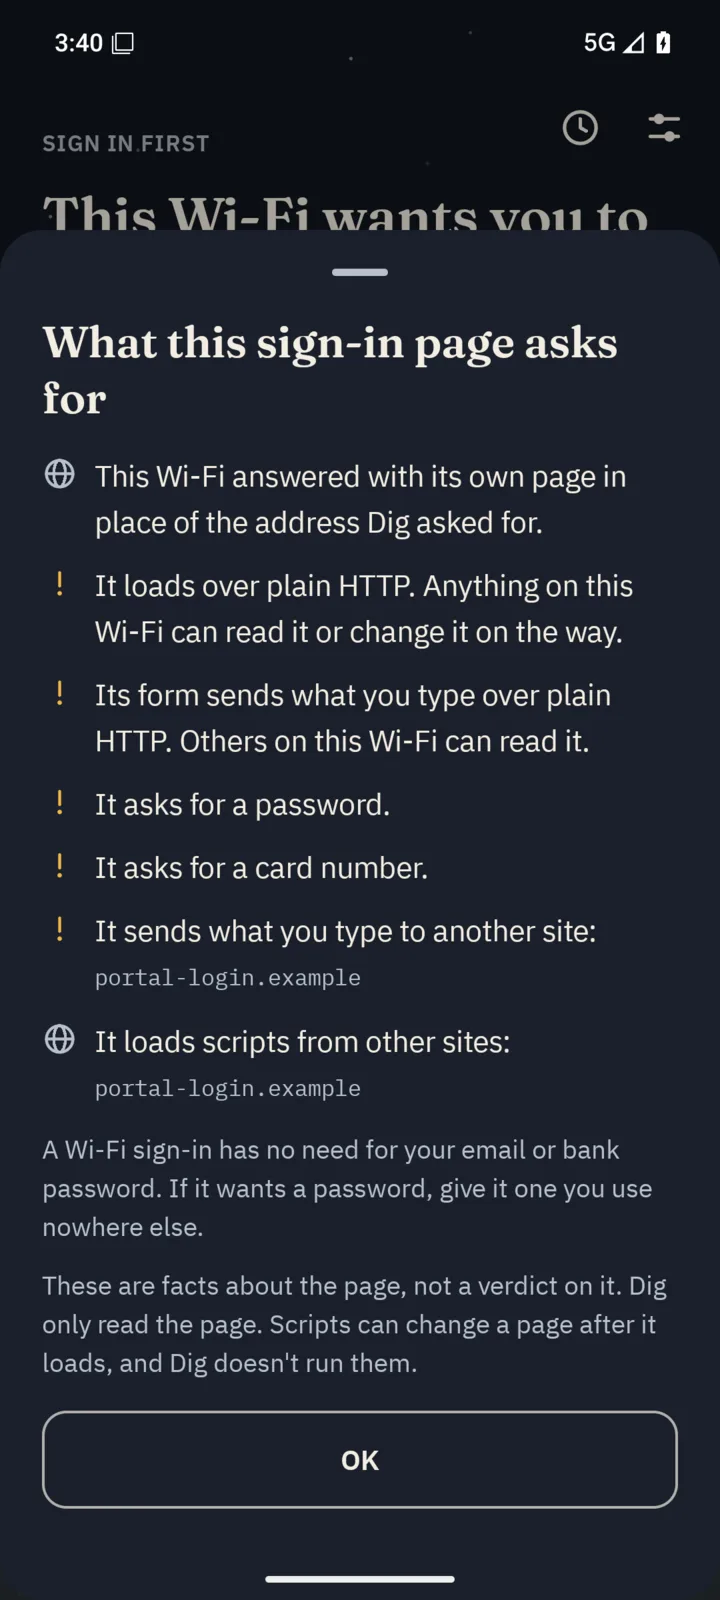
  • A sheet titled What this sign-in page asks for. It loads over plain HTTP, asks for a password and a card number, and sends what you type to another site.
    Read this sign-in pageFacts about a Wi-Fi sign-in page, read without typing anything into it. This is the demo kit's page.
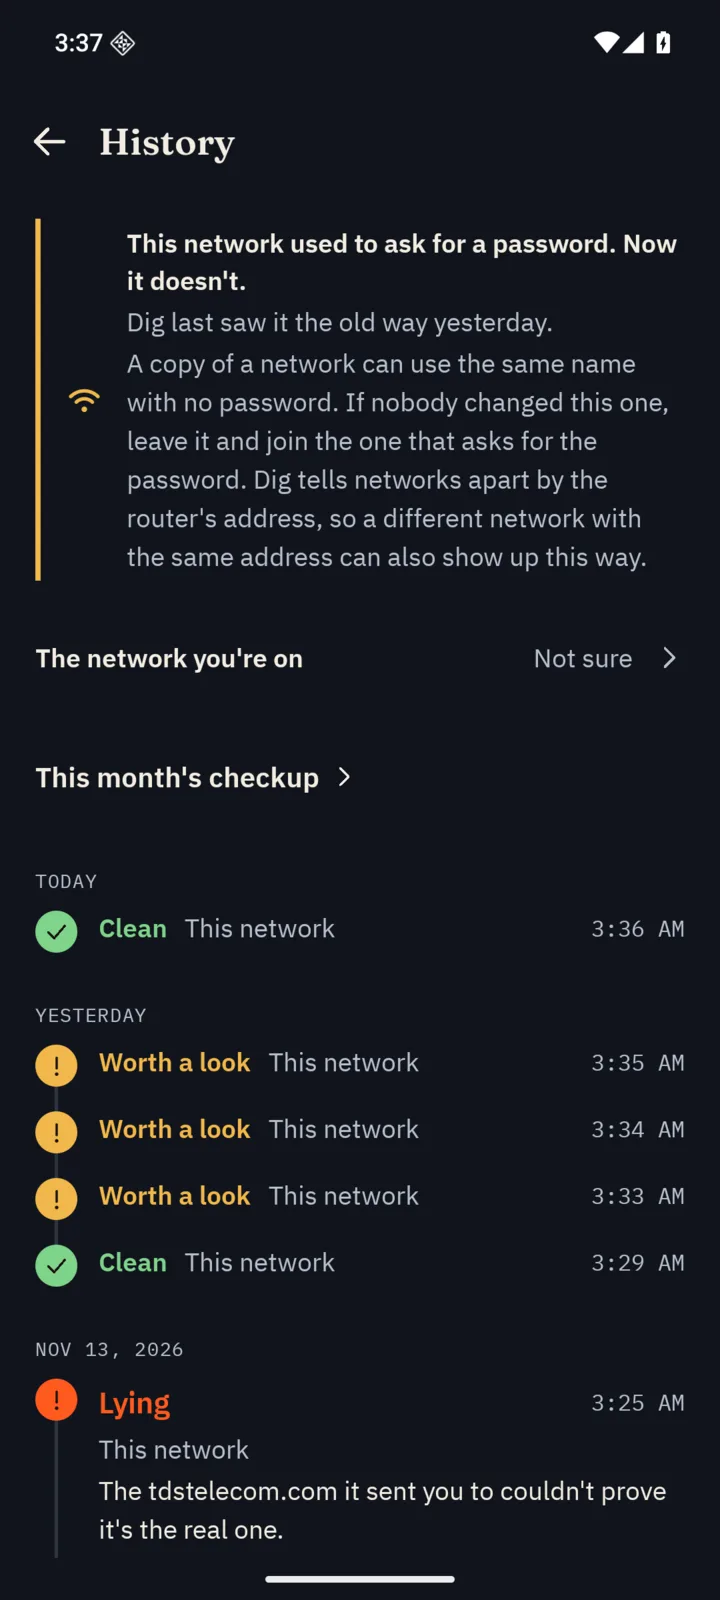
  • The history screen with a banner: this network used to ask for a password. Now it doesn't.
    Changed termsA network that used to ask for a password and now doesn't. Staged by editing the stored history.
  • The Internet layer sheet with an amber line: this network gave the right addresses, but tdstelecom.com and owl.munzzyy.dev answered with certificates this phone doesn't trust, all from the same issuer.
    At the real addressesThe addresses were right, and something in between answered for the sites anyway. Staged by redirecting them to the demo page.
  • The ticket sheet before sending, showing the plain summary and a note that Owl signs the report with a key that stays in this phone.
    A sealed ticketThe exact summary that will be sent. The report is signed on the phone and time-stamped.
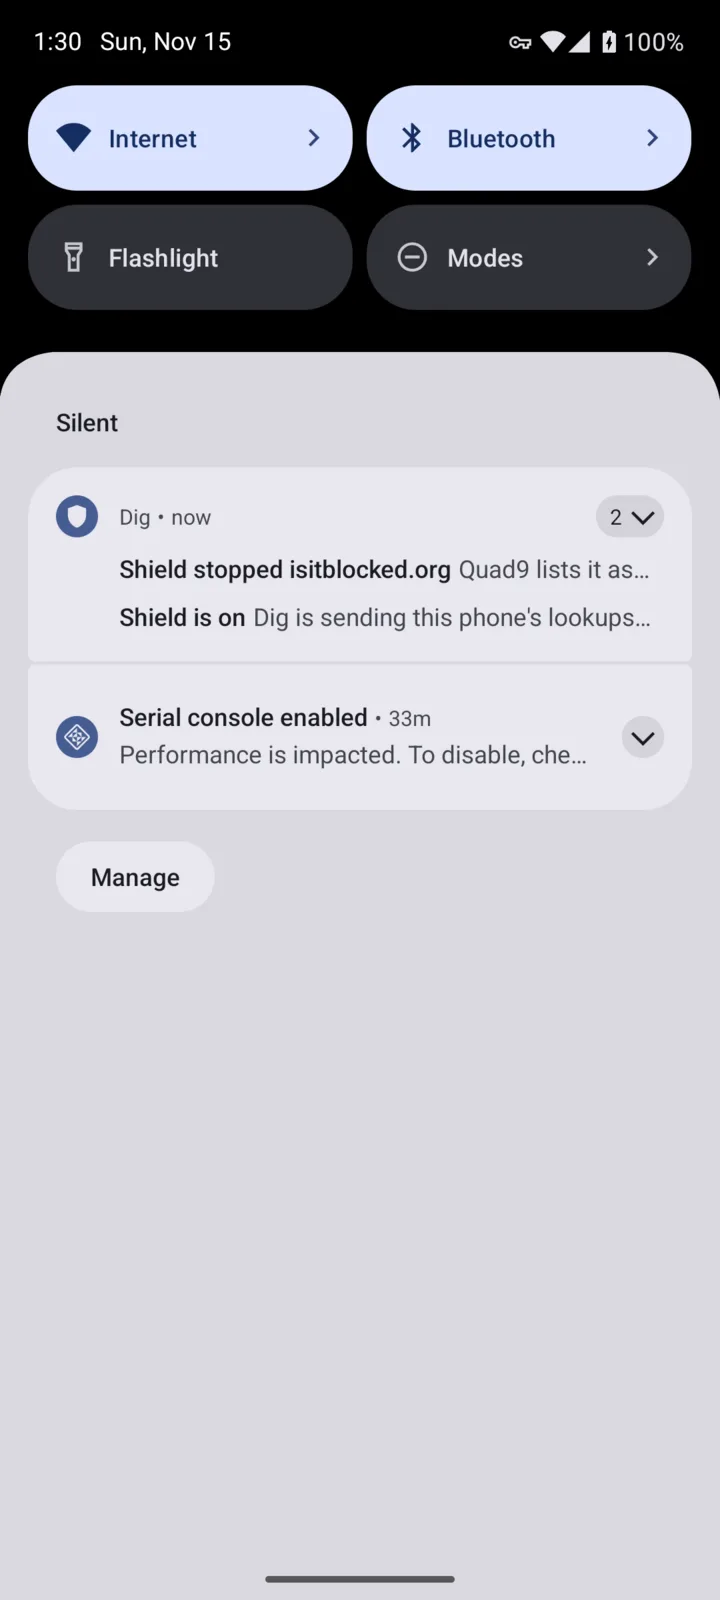
  • A notification that reads Shield stopped isitblocked.org, Quad9 lists it as a threat.
    Known bad sitesWith the option on, Shield uses providers that refuse known bad sites. This is Quad9's own test name.
  • The proof screen with a card that says this server was listed in the NCSC's April 2026 advisory on APT28.
    Named in an advisoryThe DNS server here is on the NCSC's list. This shot was staged with an address from the advisory, pointed at my own demo server.
  • Owl's main screen saying this Wi-Fi wants you to sign in first, with a Dig anyway link.
    Sign in firstOn a Wi-Fi with a sign-in page, Owl holds until you have signed in.
  • A sheet titled From support with the router fix guide from the paired desk.
    From supportThe fix guide the support desk sent. It opened by itself.
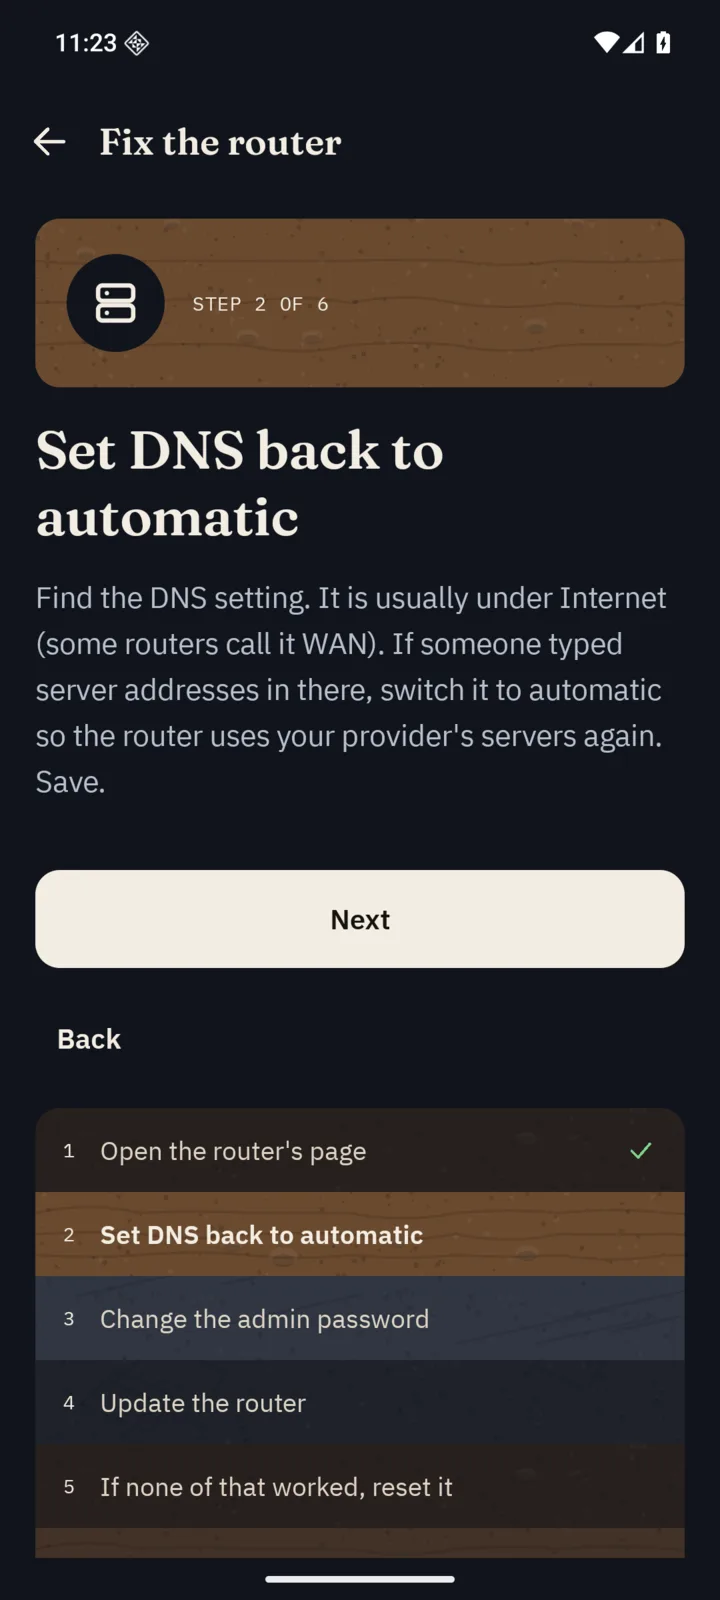
  • One step of the router fix guide.
    Router fix guideSix steps, one per screen, then a fresh dig to check.
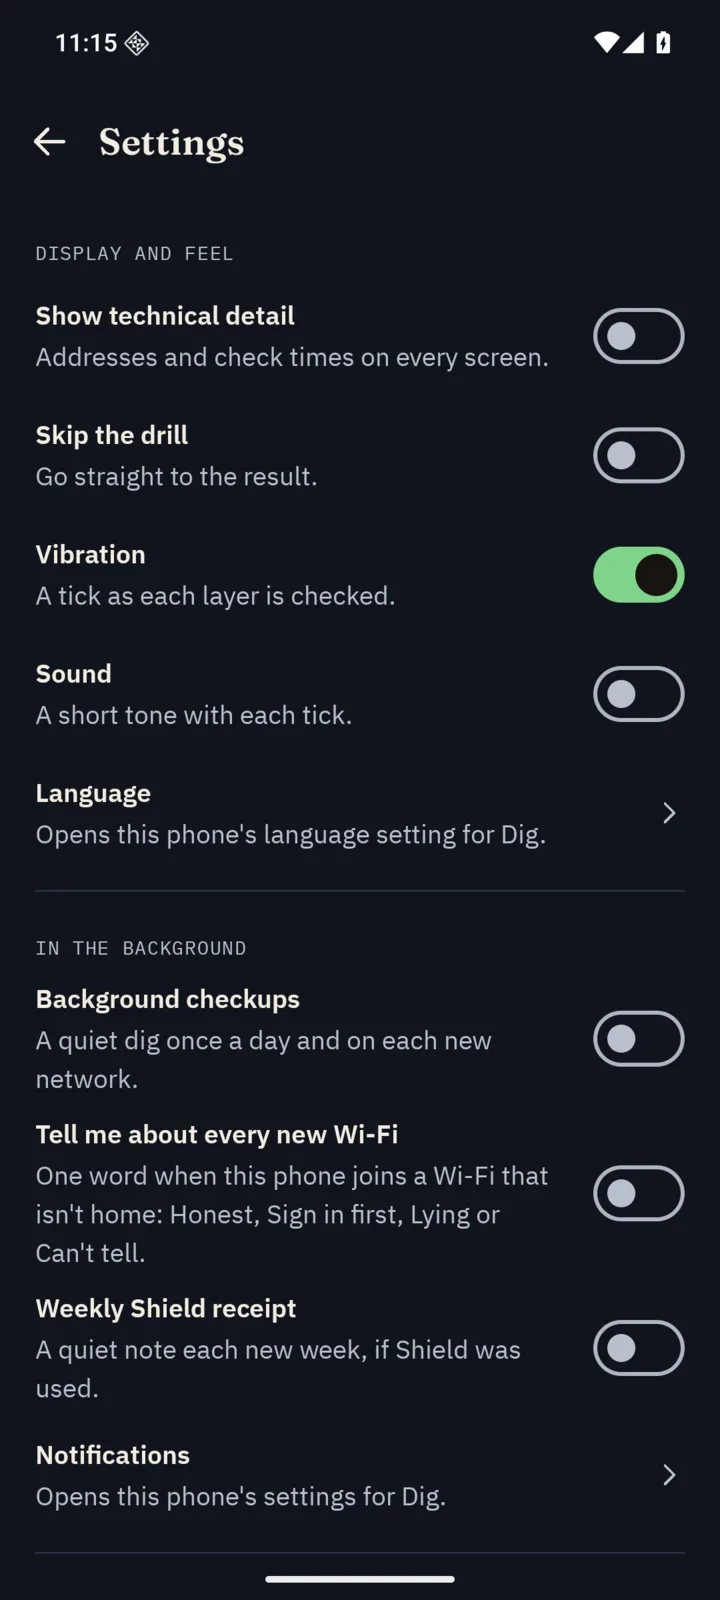
  • The settings screen, with switches for technical detail, skipping the drill, vibration and sound, and the background options.
    SettingsOne page. Technical detail, the drill, vibration, sound, language and what runs in the background.
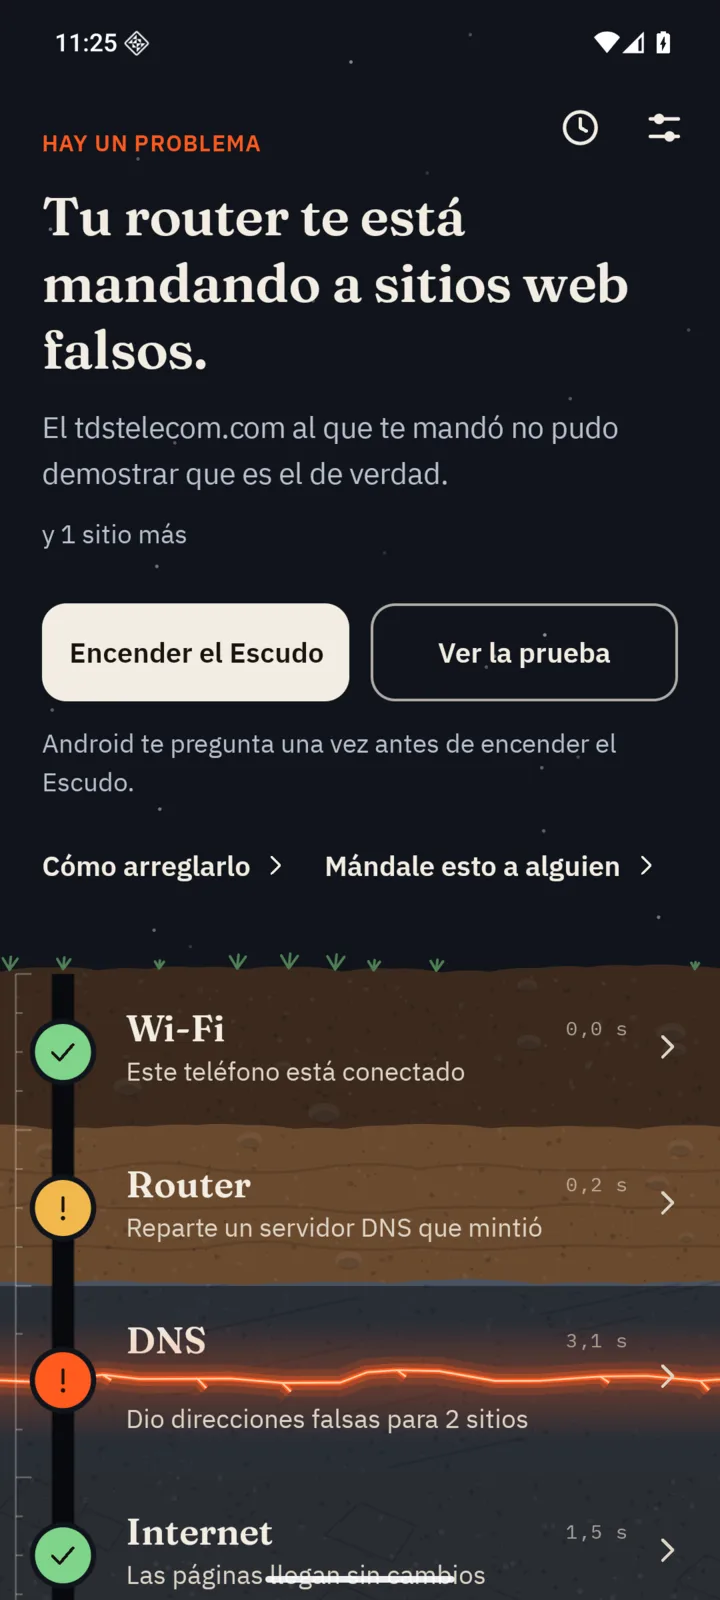
  • Owl's main screen in Spanish.
    SpanishThe screens follow the phone's language. Ticket summaries stay in English so the agent can read them.
  • Owl at the largest system font size.
    Largest fontStill readable at the largest system font size.
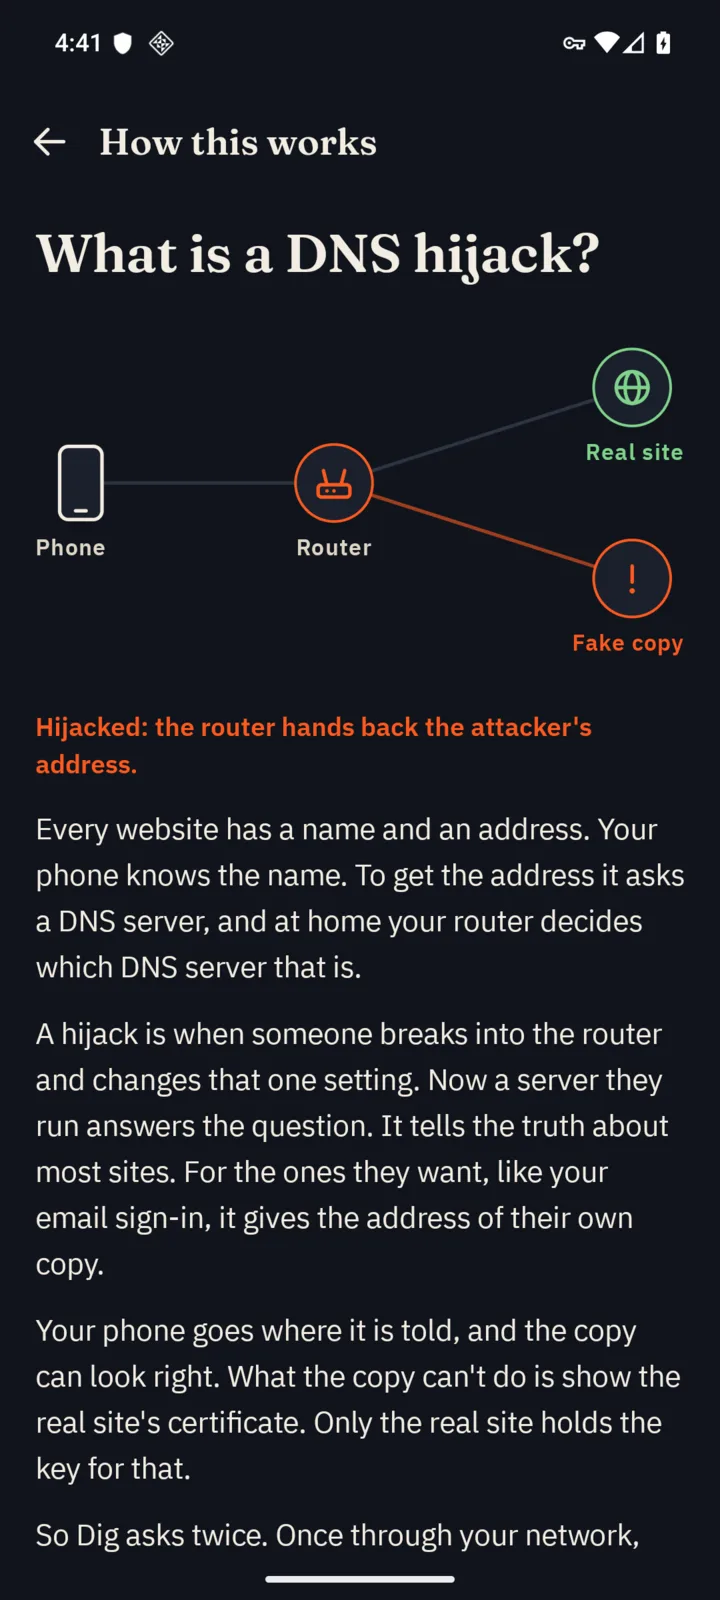
  • The learn page: a drawing of a phone, a router, the real site and a fake copy, above a short explanation.
    LearnWhat a DNS hijack is, in about thirty seconds of reading.
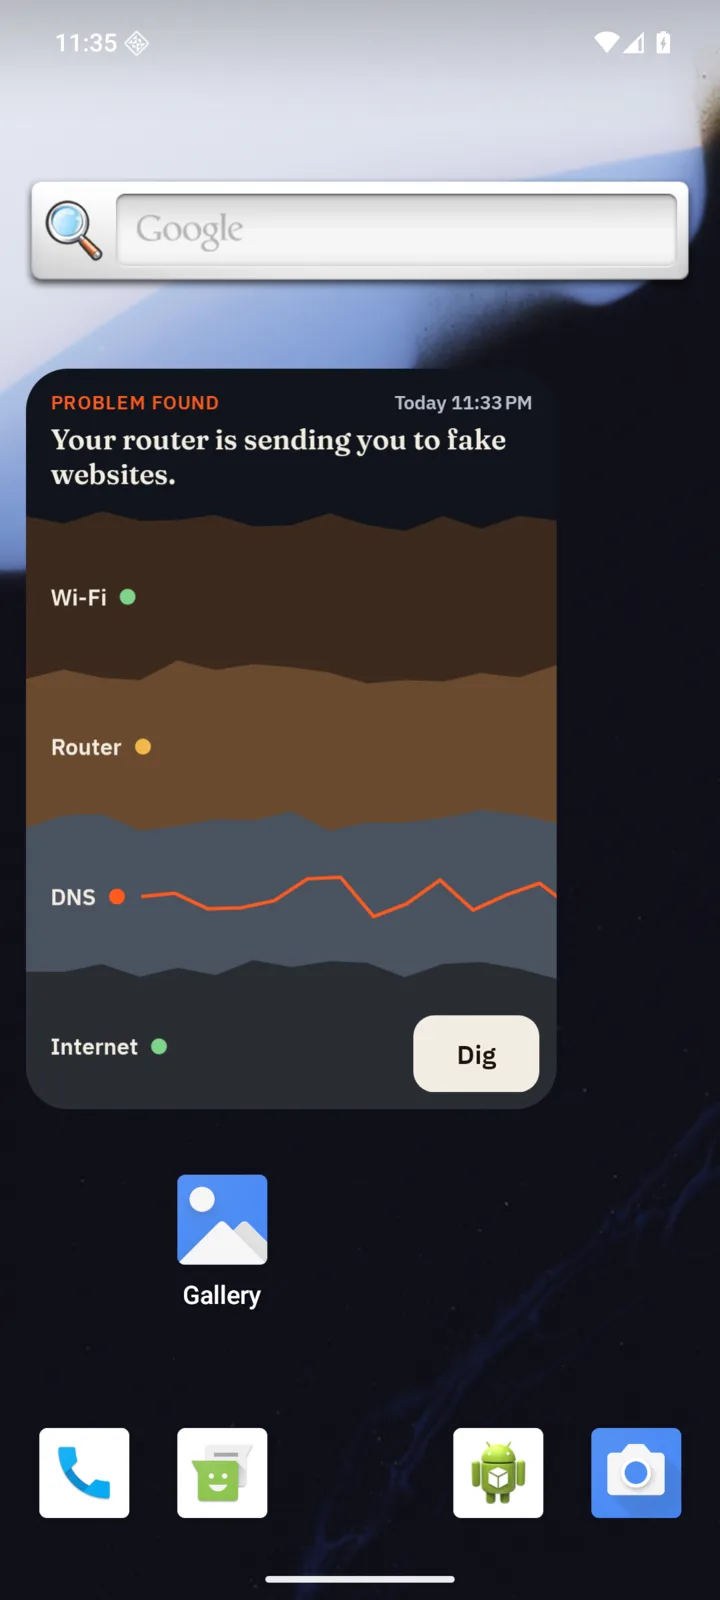
  • Owl's home screen widget showing a problem found at the DNS layer, with a Dig button.
    WidgetThe home screen widget: the layers, the last result and the day it is from.
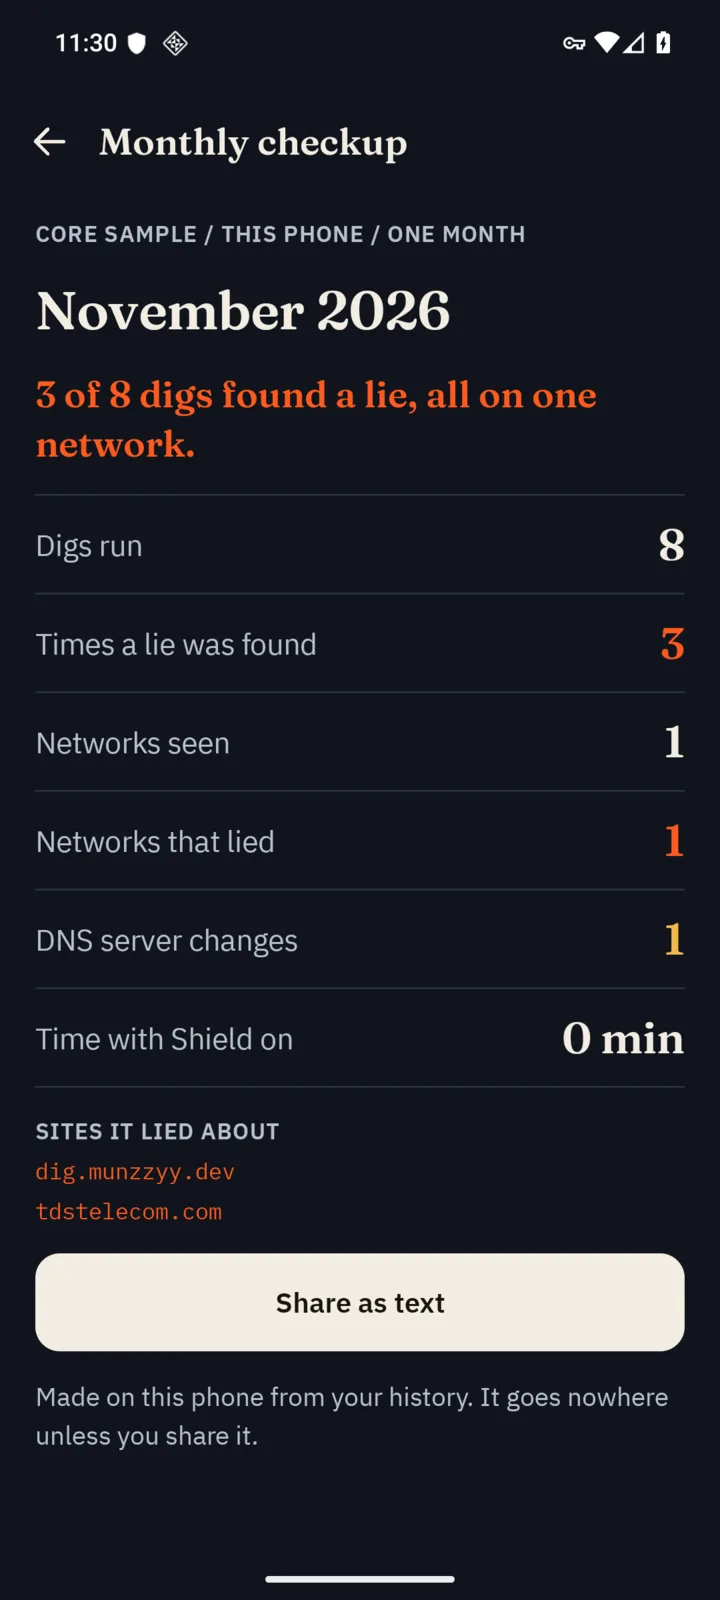
  • The monthly checkup: digs that found a lie, networks seen, DNS server changes and time with Shield on.
    Monthly checkupA month added up on the phone. It goes nowhere unless you share it.
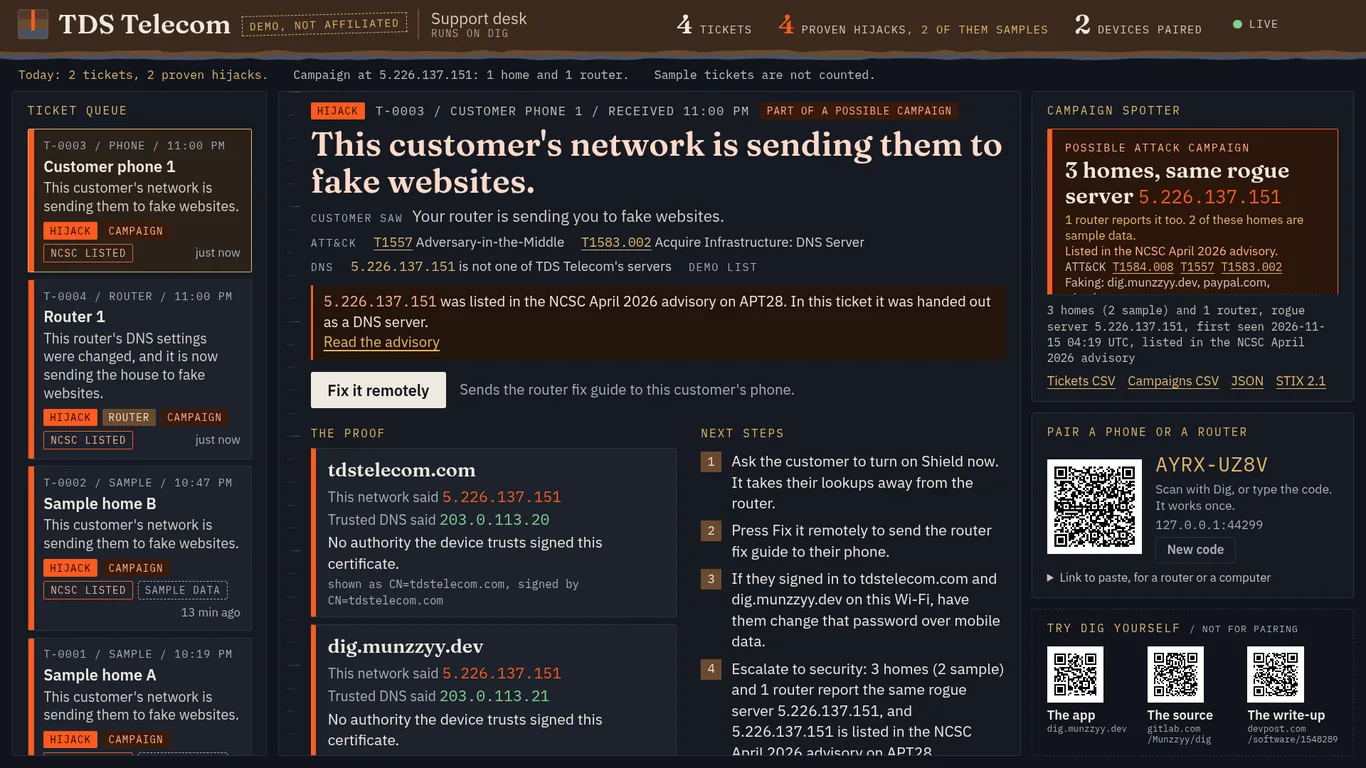
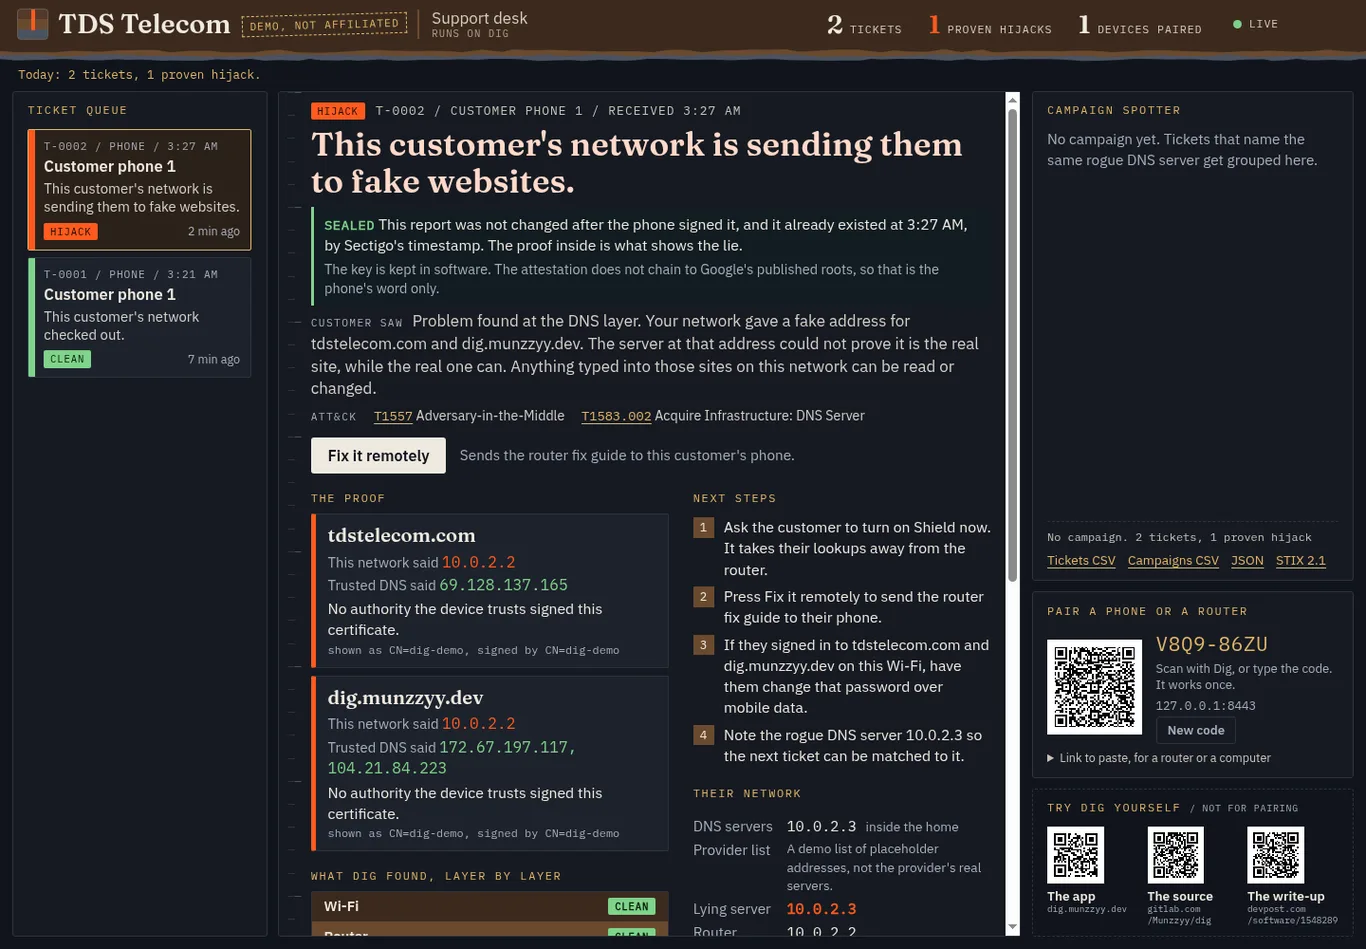
The support desk web page. A ticket queue on the left with a phone ticket, a router ticket and two sample tickets, each tagged NCSC listed. The open phone ticket reads This customer's network is sending them to fake websites, with what the customer saw, its ATT&CK techniques, a line that the DNS server is not one of the provider's, the NCSC advisory line and the proof. On the right, a possible attack campaign of three homes, the export links with STIX 2.1, the pairing code and three try-it QR codes.
Support deskThe support desk with a phone ticket open. I posted the phone and router tickets by hand, and the other two are sample data, which the header says. All four point at the first address on the NCSC list, so the picture shows what a match looks like. The TDS name is the demo config. Open the picture to see it full size.
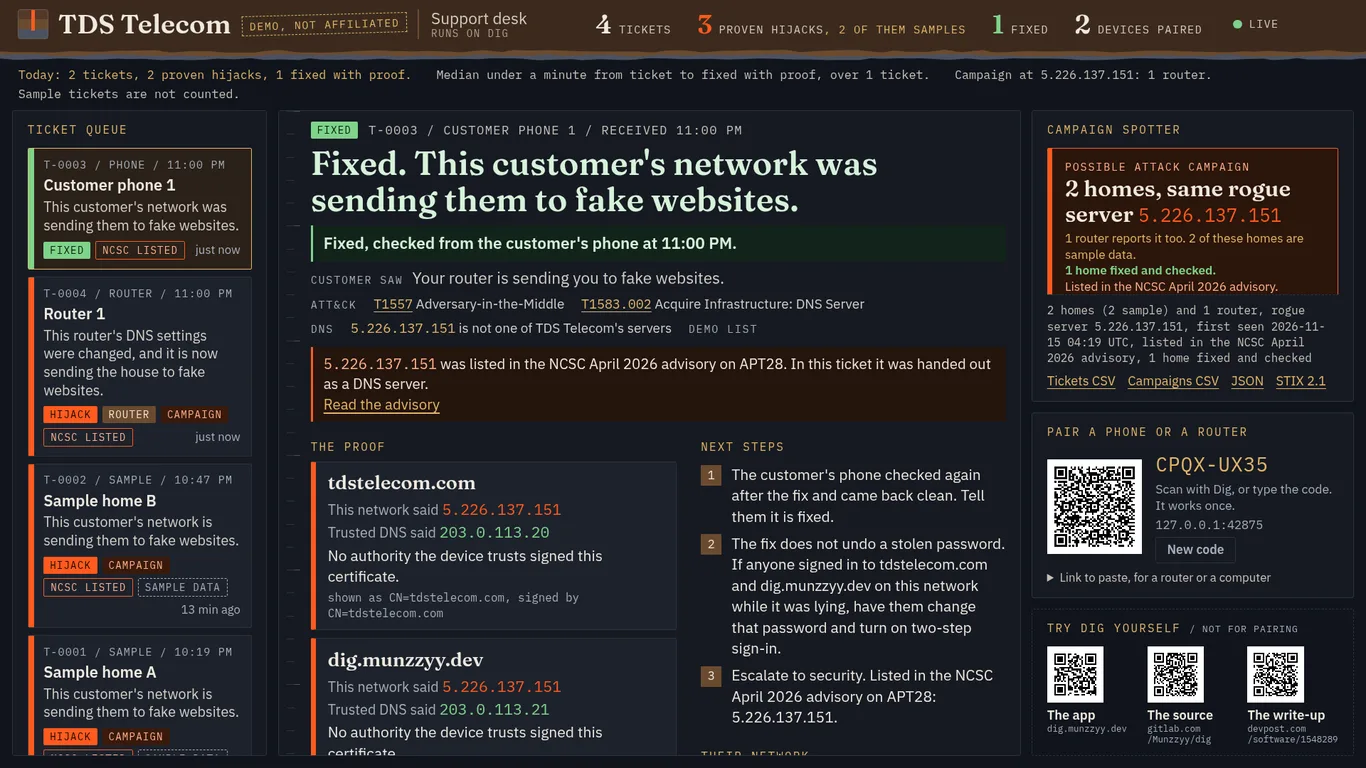
The support desk with the ticket marked Fixed. The headline reads Fixed, this customer's network was sending them to fake websites, and under it: Fixed, checked from the customer's phone at 11:00 PM.
Fixed, with proofThe same ticket after a clean second dig was posted to it. Posted by hand here. The phone doing it for real is in the phone pictures above. Open the picture to see it full size.
The support desk with a ticket marked Sealed: this report was not changed after the phone signed it, and it already existed at 3:27 AM, by Sectigo's timestamp. A second line says the key is kept in software.
A sealed reportA ticket sent from the app on an emulator. The desk checked the signature and Sectigo's time stamp. The emulator keeps its key in software, and the desk says that too. Open the picture to see it full size.

Sample 05 / Lab results / Measured

Measured, not claimed

Every number in this section comes from a run. The first accuracy run found a false alarm. I changed the rule, left the list alone, and ran it again.

Accuracy, from docs/ACCURACY.md

Sites checked through honest DNS
154: 100 popular, 54 from the app's list
Honest DNS services used
5
False alarms on honest DNS
0 in 770 checks
Warnings from the five checks that ride along
0 in 50 runs
Connections at the real addresses
0 warnings in 10 honest runs, 5 of 5 caught
App's own list: lies caught
20 of 20, then 54 of 54
Popular sites: lies caught
20 of 20, then 98 of 100
Run on
November 15, 2026, 08:39 UTC, on a computer. The third run of the night. A fourth run at 16:39 UTC, on the final engine of the day, gave the same headline.

Fuzzing, from fuzz/RESULTS.md

Parts of the code under fuzz
20, of which 16 were in the long runs
Broken inputs thrown at them
29,871,925,304
Length of the longest run
151 minutes
Bugs it found
7
Of those, fixed in the code, with a test
7 of 7
Crashes since the fixes
0 in 26,154,628,408 inputs

Checks

High findings from Android lint and semgrep
0
Tests passing
1,645 of 1,655
STIX 2.1 export, OASIS validator, strict
valid
Phones and Android versions it has run on
A Galaxy S22 at MadHacks, for the build from the morning of November 15: the catch, the proof, Shield, pairing and a ticket. The build after it, with the detail-view notes, on an Android 16 emulator. Earlier rounds on Android 10 too.

24 of the 100 popular names have no address at all, so each honest run compares 76 of them. All 54 on the app's list have one. The 2 lies that only got a warning are names whose real servers hold no valid certificate for the bare name either, so a bad one proves nothing. Nothing the liar told passed as clean. When the liar lied about all 100, 26 of the 98 called fake had no real certificate to compare with, so Owl went on the bad certificate alone. The run used the same engine as the app on a computer, not on a phone, and that measurement has not been repeated on a phone. The check for caught DNS has never met a real network that does it. I tested it with other DNS services standing in, and it caught 5 of 5. Ten of the 1,655 tests need a live network and are skipped. The made-up names check has no honest number yet: my desk's firewall drops the replies, so its quiet runs prove nothing. No IPv6 answer was called fake, but no IPv6 handshake could finish from this desk either, which is why that check only warns. Lint reports 0 errors and semgrep rated nothing high on Saturday. The validator ran with one check turned off, the one that wants a hash on every outside link. The story and the limits are in docs/ACCURACY.md.

The fuzzer feeds Owl DNS answers, packets and certificates that are broken on purpose, and checks that it never falls over. None of the 7 bugs was a way to take over the phone. Each one turned an odd input into a crash. All 7 are fixed in the code, and the 17 inputs that used to fail are kept and pass. The four newest targets have had short passes only. Eight inputs in the clean count were flagged by a check in the fuzzer that I wrote wrong, and none was a fault in Owl. Twenty-six billion clean inputs means the parsers hold up against a lot of random damage. It is not a proof.

Sample 06 / Privacy and limits / Plain words

What Owl keeps private, and what it can't catch

Privacy

  • The checks run on the phone. There are no accounts and no analytics.
  • There is no crash reporting in it, and no third-party code that phones home.
  • Your reports leave the phone only when you send them.
  • Owl never asks for your location or your contacts.
  • History stays on the phone and is kept out of cloud backups.
  • During a dig it talks to these and nothing else: the DNS server your network hands out; Cloudflare at 1.1.1.1 and Google at 8.8.8.8 over HTTPS, plus Quad9 at 9.9.9.9 on Android 14 and up, and each one's second address if the first is down; 1.1.1.1 and 8.8.8.8 on plain port 53, one question each; your router's telnet and settings page ports, one connection each with nothing sent; port 443 of the address your network gave for a site and of the address encrypted DNS gave for it, only when the two differ; connectivitycheck.gstatic.com, for one plain HTTP request; and rdap.org with the regional registry it redirects to, to look up who owns the network's DNS server, only when that server is a public address Owl doesn't know. On Wi-Fi it also asks the local network, and nobody past it, for three made-up names; makes one request to the router's own page; and connects to three of the sites at their real addresses.
  • Three things happen only after a tap. The mobile data check asks Cloudflare and Google over mobile data. Why won't this site load? looks up the one name you gave it. Read this sign-in page fetches that page and sends it nothing.
  • Sealing a ticket sends a fingerprint of the signature to timestamp.sectigo.com. The report itself goes only to the desk.
  • The NCSC list comes inside the app. Matching against it looks nothing up.
  • Owl never looks up your public address and never sends it anywhere. One question to Google can come back with it in the answer. Owl reads that answer to see who gave it, then drops it.
  • With Shield on, the phone's lookups go to the provider you picked, or to Quad9 and Cloudflare's security service if you turned on blocking. A desk you paired with gets a ticket only when you send one. After that the app asks that desk for a fix guide for three minutes.
  • This website sets no cookies, runs no scripts, and loads nothing from anyone else.

What Owl cannot catch

  • A lie about a site it didn't check. Owl checks 54 sites, most of them sign-in pages, plus the ones you add. A router that lies about one other name slips past.
  • A relay that passes you through to the real site. It gives a different address, but the certificate is the real one, so Owl will not call it fake.
  • A valid certificate issued to the wrong party. If a certificate authority is tricked, the fake server passes the check.
  • A phone that is already taken over. Owl trusts the phone it runs on.
  • A network that blocks all encrypted DNS. Owl tries two addresses for each provider. If all are blocked it gets no honest answer to compare with. It warns you, and Shield can't work there. With your say-so it can check over mobile data.
  • A copy of your Wi-Fi. Telling a look-alike network from the real one needs the location permission. Owl never asks for it. The closest it gets is noticing that a network stopped asking for a password.
  • Something that intercepts every secure connection. Then the answers look unsettled and Owl warns, but it can't name what is in the way.
  • The router's internet-facing side. The phone sees the router from inside the home. Owl Guard reads that side on the router itself.
  • A server nobody has listed yet. The NCSC list is from April 2026. No match only means the address isn't on it.
  • The other devices in the house. Shield covers the phone it runs on. Everything else stays exposed until the router is fixed, or Owl Guard is on it.

What Owl catches and what it can't: every attack I mapped, the ways around the proof that I know about, and what no phone can see.

Sample 07 / Take one home / Android

Download

Owl is free software. Take the signed APK, or read the code and build it yourself.

Download owl.apk

To install it, open the file on your phone and allow your browser to install unknown apps when Android asks. It needs Android 10 or newer.

No Android phone? Check this network from any browser, iPhone included. A browser can't see DNS answers, so it can't prove a lie, but it shows which of the 54 sign-in sites it reached with their real certificates. On a computer, run the laptop check.

SHA-256 of owl.apk
c534ef618558ca938b31235080da62388a4be3863fd190db68904c890a99862f
License
GPL-3.0-or-later